Category: Guard Management

  • Inventory Reconciliation: What Security Teams Must Check

    A spreadsheet can say a site has twenty radios in stock. The shelf might have seventeen. Inventory reconciliation is the process that closes that gap: comparing what the system records against what is physically on site, by location, so a shortage shows up before it costs a shift its equipment rather than after.

    Inventory reconciliation is the process of comparing recorded stock levels at each location against a physical count, so differences are flagged and corrected rather than left to accumulate unnoticed.

    The problem with trusting the stock number on screen

    Stock levels drift from reality in small, unremarkable ways: an item is used but never logged as removed, a transfer is only half-recorded, someone borrows a torch and forgets to note it. None of these on their own looks like a problem. Over months, the recorded count and the real count stop matching and nobody notices until a shift turns up short on equipment it was supposed to have.

    Manual reconciliation, counting every item on a shelf and checking it against a spreadsheet, is slow enough that most sites only do it once a year, by which point the gap has had a long time to grow.

    Why it matters

    A security company cannot staff a shift properly if the equipment it is counting on is not actually there. Reconciliation is also what protects the integrity of every other inventory process: a transfer, an issue, a threshold alert, all depend on the starting stock count being accurate. If the baseline is wrong, everything built on it is wrong too.

    How it works in AVES

    AVES keeps stock levels per location, with a minimum threshold set per item. Every add, remove, transfer, send-to-location or return-to-main action is kept in the item’s movement history. A physical stocktake is run by scanning items against that recorded history, reconciling what should be on site with what is actually confirmed on site, rather than counting by hand against a printed sheet. A sync/reconcile endpoint lines the two sides up directly, flagging any mismatch instead of silently accepting whichever number was entered last.

    This is a different process from tagging and scanning a serialised asset such as a CCTV unit or radio through its individual lifecycle (covered in our asset tagging software guide). Inventory reconciliation works on bulk stock counts per location; asset tracking works on one tagged item at a time. A site can need both.

    What to check during an inventory reconciliation

    1. Recorded stock level versus physical count, per item, per location. The core comparison: what the system says is there against what is actually there.
    2. Minimum threshold status after the count. Whether the confirmed count has already dropped below the threshold that should have triggered a restock.
    3. Unreconciled movement history entries. Any add, remove or transfer logged but not yet reflected in the count being checked.
    4. Pending transfers in the approval queue. Stock that is mid-transfer should not be double-counted at both the origin and destination location.
    5. Items issued to a person and not yet returned. These are out of the location’s stock temporarily and should be checked against their expected return date, not counted as missing.
    6. The size and direction of any mismatch. A shortfall and a surplus point to different causes, unlogged use versus an unlogged delivery, so the direction matters as much as the number.

    What a reconciliation actually fixes

    A reconciliation does not just produce a corrected number. It produces a trail: which item was wrong, by how much and at which location, logged against that item’s movement history rather than quietly overwritten. That trail is what turns a one-off count into a pattern a manager can act on, instead of a number that resets to “unknown” the moment the next stocktake begins.

    Common mistakes in inventory reconciliation

    • Only reconciling once a year. The longer the gap between counts, the more causes pile up and the harder it is to trace any single discrepancy back to what actually happened.
    • Counting stock that is mid-transfer as missing. A pending transfer in the approval queue is not lost stock; it is stock in motion that has not cleared yet.
    • Ignoring small, repeated mismatches. A one-off gap might be a counting error. The same item coming up short every month points to a real process gap, not noise.
    • Reconciling the count but not the threshold. Confirming the physical number without checking it against the minimum threshold misses the point: the number existing is not the same as the number being enough.
    • Treating reconciliation as a stock-only exercise. An item issued to a person with no logged return date is not a reconciliation gap; it needs following up as an overdue issue, not written off against the count.

    Frequently asked questions

    How often should inventory reconciliation happen? Scanning-based reconciliation is fast enough to run far more often than an annual manual count. The more frequent the check, the smaller and easier to trace any mismatch stays.

    Is inventory reconciliation the same as an asset stocktake? Both use a scan-to-reconcile approach, but they check different things. Inventory reconciliation checks bulk stock levels per location. Asset tracking (see our asset tagging software guide) checks individually tagged, serialised items one by one.

    What happens to stock that is in transit between sites during a reconciliation? A transfer still in the approval queue should be tracked separately from each location’s confirmed count, not counted as missing at the origin or surplus at the destination. See our stock transfer form guide for how a transfer is recorded end to end.

    Does reconciliation flag items below their minimum threshold? Yes, checking the confirmed count against each item’s minimum threshold is part of a proper reconciliation, not a separate step done later.

    What should happen when a reconciliation finds a mismatch? The mismatch should be logged against the item’s movement history with its size and direction, so a pattern across months can be spotted rather than treating each gap as an isolated incident.

    Does a smaller site still need a reconciliation process, or just a single location? Yes. Even a single-location operation benefits from the same scan-to-reconcile discipline: the minimum threshold and movement history work the same way whether a company runs one site or fifty, and a small operation that skips reconciliation is just as exposed to a quiet drift between its screen and its shelf.

    Where reconciliation fits in your wider inventory operations

    Inventory reconciliation is the check that keeps everything else in our inventory management software overview honest, including every stock transfer and the financial view in our fixed asset register guide. The same scan-to-reconcile discipline is worth comparing with how serialised equipment is tracked in our asset tagging software guide, and with the kind of gaps a security guard audit checklist is built to catch on site.

    If your stock counts and your shelves have stopped agreeing with each other, book a 30-minute demo and we will show you the actual scan-to-reconcile stocktake and sync/reconcile screen.
    Book a demo or start a free trial.

  • Stock Transfer Form: What Security Companies Must Record

    A security company running more than one site moves bulk stock between them constantly: uniforms heading to a new deployment, radios reissued from a site that is winding down, torches sent to cover a shortage. A stock transfer form is the record that stops that movement from becoming a guess. It captures where stock came from, where it is going and who signed off on both ends, so a missing box of radios is a lookup instead of a mystery.

    A stock transfer form is a record of bulk stock moving between locations: the origin and destination sites, the items and quantities involved and a dispatch and receipt sign-off at each end, kept separate from a one-off issue to a single person.

    The problem with moving stock between sites informally

    Most security companies move stock between sites the easy way: a supervisor puts a box of uniforms in a van and tells the receiving site it is coming. Nobody logs the quantity. Nobody confirms it arrived in full. A week later the sending site’s stock count looks wrong. The receiving site insists they never got the missing items, and there is no record either way to settle it.

    This is the same problem a per-location inventory system is built to prevent, but only if the transfer itself is logged, not just the stock levels before and after it.

    Why it matters

    Bulk stock sitting at the wrong site or quietly short at the site that needs it is an operational problem before it is a financial one: a site running low on uniforms or radios cannot cover a shift properly. A transfer form also protects both ends of the move. If a dispute comes up about what was sent versus what arrived, the form is the record, not someone’s memory of a phone call.

    How it works in AVES

    AVES tracks stock per location, with a minimum threshold set for each item at each site, so a site running low is visible before it runs out. Moving stock is handled as one of several defined actions: add, remove, transfer, send-to-location or return-to-main. Each of these actions is kept as part of the item’s movement history, not just a changed number.

    A transfer between locations goes through an approval queue rather than updating silently: it is requested, then approved, before the stock levels at either site change. Where stock is issued to a named person rather than moved between locations, the system separately tracks an expected return date and the condition the item comes back in. A sync/reconcile endpoint keeps the recorded levels lined up with what a stocktake confirms is actually on site.

    What a stock transfer form must record

    1. Origin location. The site or store the stock is leaving, so the sending location’s count can be reduced correctly.
    2. Destination location. The site or store the stock is going to, so it lands in the right place’s count, not just “somewhere else.”
    3. Items and quantities. Exactly what is moving and how much, matched against what each site actually has on its shelves.
    4. Transfer type. Whether this is a transfer between two locations or a send-to-location/return-to-main movement, since each affects stock levels differently.
    5. Approval status. Whether the transfer has been requested, approved or is still pending, since stock levels should not change until it clears the approval queue.
    6. Movement history entry. A record of the action itself, kept against the item, not overwritten the next time it moves again.
    7. Minimum threshold check. Whether the move drops the origin site below its minimum stock threshold, which should trigger a restock conversation before it becomes a shortage.

    Common mistakes with stock transfers

    • Treating a transfer like a casual favour between sites. If it is not logged as a transfer, the stock levels at both ends go out of sync the moment it moves.
    • Skipping the approval step. Letting stock levels update before a transfer is approved means a mistaken or unauthorised move is already baked into the record.
    • Mixing up transfers with issuing to a person. A transfer moves stock between locations; issuing an item to a named person is a different action with its own expected return date and condition. Recording one as the other breaks both histories.
    • Only checking stock levels, never the movement history. A level tells you what is there now. The movement history tells you how it got that way, which is what you need when a dispute comes up.
    • Letting a site run below its minimum threshold without transferring in time. The threshold exists to flag a shortage before a shift is short-staffed on equipment, not after.

    Why a transfer form earns its place next to a spreadsheet

    A spreadsheet can list what a site is supposed to have. It cannot show who moved what and when, or whether the receiving site actually confirmed the delivery. A transfer form exists precisely to close that gap: it ties a single movement to an origin, a destination, an approval and a receipt, so the record survives even after the supervisor who carried the box has moved on to something else. For a company running several sites with shared stock pools, that record is often the only thing standing between a clean handover and a finger-pointing exercise over missing uniforms.

    Frequently asked questions

    Is a stock transfer form the same as a gate pass? No. A transfer moves bulk stock between two sites or stores inside the inventory system. A gate pass covers items physically leaving through a site’s gate, with issue and return photos. If stock is crossing a site boundary through a gate, see our gate pass format guide.

    Does a transfer need approval before stock levels change? Yes, in AVES a transfer goes through an approval queue. Stock levels at the origin and destination only update once the transfer is approved, not the moment it is requested.

    What is the difference between a transfer and issuing stock to a person? A transfer moves stock between locations. Issuing stock to a person is tracked separately, with an expected return date and the condition the item comes back in, because the accountability sits with an individual rather than a site.

    How does a transfer affect minimum stock thresholds? Each location has its own minimum threshold per item. A transfer that drops the origin site below its threshold should be visible immediately, so a restock can be arranged before the shortage affects a shift.

    Can a transfer be reconciled against a physical count? Yes. The sync/reconcile endpoint lines up what the system recorded through transfers and other movements with what a physical stocktake actually finds on site. See our inventory reconciliation guide for how that check works.

    Who should be able to approve a transfer? AVES does not fix this to one role; the approval queue is simply a required step before stock levels change. In practice, most security companies route approval to whoever is accountable for the receiving site’s stock, so the person confirming receipt is the same person confirming the count is correct.

    Where stock transfers fit in your wider inventory operations

    A stock transfer form is one part of the per-location stock picture covered in our inventory management software overview. It sits next to inventory reconciliation for checking that transfers landed correctly, and alongside the serialised-equipment tracking in our asset tagging software guide and the financial view in our fixed asset register guide. The same discipline of logging a move rather than assuming it happened is worth comparing with how AVES handles daily guard activity in the security guard logbook.

    If your sites are moving bulk stock between each other without a shared record, book a 30-minute demo and we will show you the actual transfer request, approval queue and movement history screens.

    Book a demo or start a free trial.

  • Safety Committee Minutes Template: 8 Fields to Include

    Safety Committee Minutes Template: 8 Fields to Include

    A safety committee minutes template is a fixed record format a security or facilities team uses to capture who attended a safety meeting, what hazards and agenda items were raised and which actions were assigned, to whom and with what status, so nothing discussed gets lost between one meeting and the next.

    Search for a safety committee minutes template and most results are generic business meeting formats that were never built for a security site. There is no field for the hazard that was raised, no owner on the action that was meant to fix it and no way to prove the same issue was not simply carried over and quietly dropped. A security safety committee has a narrower job than a general staff meeting: raise what is unsafe, assign who fixes it and show that it got fixed. The template below is built around that job.

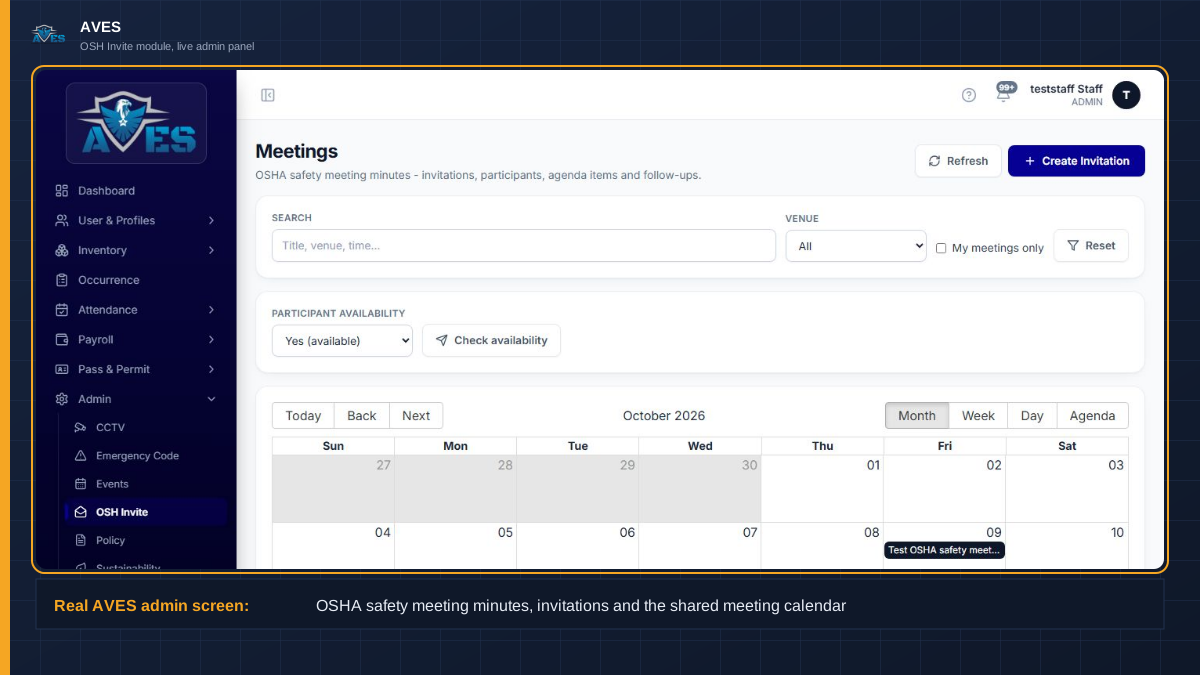
    Safety committee minutes template: real AVES OSH Invite Meetings screen showing Create Invitation, participant availability check and the shared meeting calendar

    The problem: minutes that do not survive the gap between meetings

    Most safety committees start out recording minutes in whatever is to hand: a shared document, a notebook passed between supervisors or a short email sent round after the meeting. That works for one meeting. It breaks down over several, because nobody is checking the new minutes against the old ones in a consistent way. An action raised in March shows up again in June with no note of what happened in between and nobody can say whether it was fixed, forgotten or simply never assigned to anyone in the first place.

    The gap is rarely the meeting itself. Most sites do hold the meeting. The gap is the record: a format that does not force attendance, agenda items and actions into the same comparable shape every time, so the committee cannot see its own history.

    Why it matters for a security company

    A security contractor’s safety committee is not just an internal formality. If a client auditor, insurer or regulator ever asks for proof that hazards raised on site were tracked to closure, the minutes are the evidence. A folder of inconsistent notes, with no owner or status on half the entries, does not answer that question. A consistent safety committee minutes template does, because every entry carries the same fields: what was raised, who owns it and where it stands.

    It matters for the committee too. An action with no named owner and no due date is an action nobody feels responsible for. A safety committee minutes template that forces both into every entry is what turns a safety committee from a box ticked once a month into a working part of how hazards actually get fixed.

    Safety Committee Minutes Template: 8 Fields to Capture Every Meeting

    1. Meeting date, time and venue. The basic record of when and where the committee met.
    2. Attendees present, with apologies for anyone expected but absent noted separately.
    3. Previous minutes review. The status of every action carried over from the last meeting, not a fresh blank page.
    4. New hazards, near misses or safety concerns raised this meeting, in the words of whoever raised them.
    5. Incident or inspection review for the period since the last meeting, where relevant.
    6. New action items, each with a single named owner rather than “the team” or “management”.
    7. Due date for every action. Not an open ended “soon”.
    8. Status for every item, open, in progress or closed, reviewed again at the start of the next meeting.

    AVES runs this as a dedicated OSH Invite record rather than a document someone has to remember to update. A meeting is created as an invitation with a title, venue and time. Participant availability is checked before it goes out, so the committee is not scheduled around one chair’s personal diary. Every meeting sits on a shared calendar with month, week, day and agenda views, so the next chair can see what was scheduled and when without hunting through old files.

    Inside the meeting record itself, the fields split the same way the template above does. A discussion item captures the topic and what was said about it. An action item captures who owns it and what its current status is. That split is what lets the committee open the next meeting by reviewing exactly what was still open from the last one, instead of starting from a blank page and hoping someone remembers.

    Common mistakes with a safety committee minutes template

    No fixed format. Without a safety committee minutes template, every meeting gets minuted differently and there is nothing consistent to compare one month against the next. Gaps in the record are easy to miss as a result.

    Actions with no named owner. An action assigned to “the site team” or “management” is an action nobody is accountable for closing.

    Minutes kept only on paper. A notebook in a site office is not available to the next chair, an auditor or anyone trying to check whether an old action was actually closed.

    Previous actions never reviewed. A template that only captures what is new, with no section for reviewing what was carried over, lets open items drift for months without anyone noticing.

    No link between an action and the hazard that raised it. An action item that does not reference what prompted it is hard to justify later if a client or regulator asks why it mattered.

    How AVES handles it

    AVES does not treat a safety committee minutes template as a document that lives outside the rest of the safety record. The OSH Invite module schedules the meeting, checks who can attend before the invitation is sent and keeps every past and upcoming meeting on one shared calendar. The discussion and action items captured during the meeting stay attached to that same record, so the status of last meeting’s actions is exactly where the committee left it, not buried in a separate file nobody opens between meetings.

    Safety Committee Minutes Template FAQ

    What should a safety committee minutes template include?
    At minimum: the meeting date, time and venue, who attended, a review of actions carried over from last time, any new hazards or concerns raised and every new action with a named owner, a due date and a status.

    How often should a security safety committee meet?
    Monthly is common for an active site with daily guarding activity. The right cadence is whatever matches your client contract or the audit expectations your regulator sets, rather than a fixed universal rule.

    Who should attend a safety committee meeting?
    Typically the site supervisor or safety officer, a representative of the guards or staff working the site and, where the agenda calls for it, a client or management representative.

    Is a template enough, or do I need software?
    A safety committee minutes template works for a single site with one person keeping the record straight. It tends to break down once a company runs several sites or several shifts, because a paper or document based template has no shared view across them. A digital record solves that by keeping every meeting on one calendar that any authorised chair can open.

    Does AVES include a safety committee minutes template?
    AVES’s OSH Invite module is built around exactly this record: scheduling, attendance, discussion items and action items with an owner and a status, all attached to the same meeting. See the full guide to safety committee meetings for how the record works end to end.

    Where this fits in your compliance record keeping

    A safety committee minutes template is one piece of a wider compliance record. The same discipline, a named owner, a date and a status, applies to a fire drill record, a first aid checklist and whatever a site security audit checklist expects to see when an inspector asks for proof. Where a hazard raised in committee turns into a formal incident, the same record keeping standard carries through to an incident report form, so there is one consistent trail from the meeting where a concern was first raised to however it was eventually resolved. For the full explainer on running the meeting itself, start with safety committee meetings.

    Book a 30 minute demo and we will show you how a safety committee meeting, its attendance, its discussion items and every action it raises stay on one record instead of a document nobody updates: book a demo. Prefer to explore first? Start a free trial.

    Follow AVES on Instagram for more security operations tips.

  • Training Request Form: Fields That Actually Hold Up

    Training Request Form: Fields That Actually Hold Up

    A training request form is the record that captures who asked for which training, which catalogue entry it came from and what happened to that request next. It is the input side of a security team’s training record. Without it, the only record of a training need is whatever was said out loud at the time.

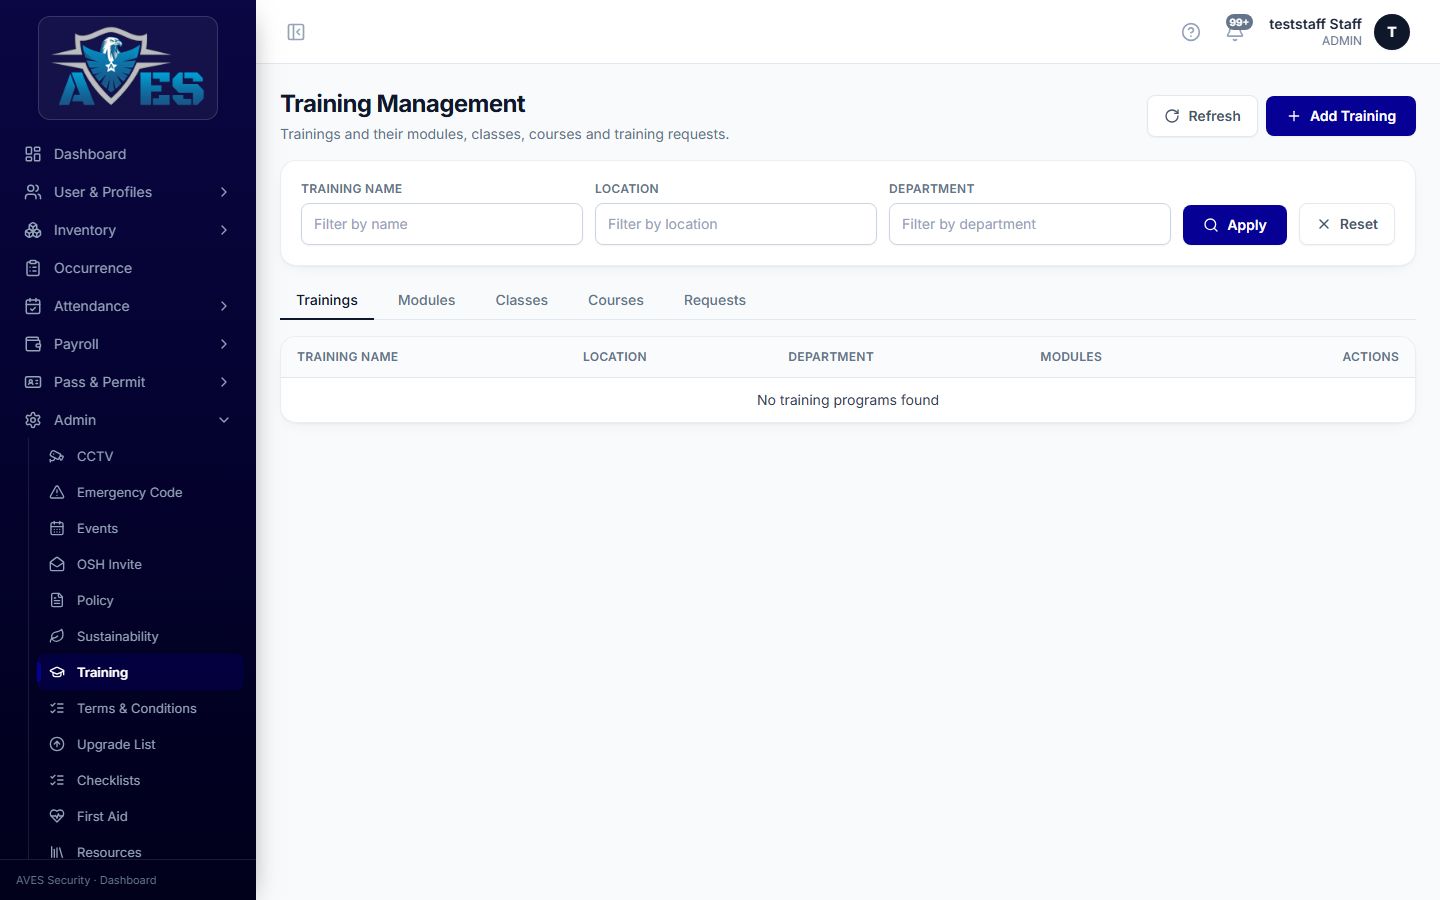
    Real AVES admin screen showing the Training module catalogue and assignment list
    The AVES Training screen: the catalogue and assignment list a request is logged against.

    Most security operators who already run a training tracker still have a gap on the other end: how does a training actually get requested in the first place. A verbal ask in the guardroom, a WhatsApp message to a supervisor or a note left for HR leaves no trail. By the time a client or an auditor asks “who asked for this training and when”, there is nothing to show them. That gap is exactly what a training request form exists to close.

    The problem with informal training requests

    Security teams run on shift patterns, not office hours. A guard who wants first aid refresher training or who needs to request a course before a licence renewal rarely has a desk or an HR portal open in front of them. So the request happens informally, by word of mouth, by text message or not at all. Three things go wrong with a training request that never became a training request form:

    • There is no fixed record of when the request was made, so it cannot be checked against how long it took to action.
    • There is no link back to a defined course in a catalogue, so two people can describe the same training differently and nobody can confirm it was the same session.
    • There is no status to track, so a request can sit unanswered for weeks with nobody accountable for it.

    Why a proper request record matters

    Client contracts for guarding services increasingly name specific training as a condition of deployment: fire warden training, first aid, use of force or site-specific inductions. If a client or a licensing body asks for proof that training was requested and actioned on a given date, a verbal request leaves the operator with nothing but a guess. A written, timestamped training request form turns that into a two-minute lookup instead of a scramble through old messages.

    It also protects the guard. If a worker requested a course and the request was never actioned, a dated record shows that the gap was on the employer’s side, not the worker’s.

    How the request works inside AVES

    AVES ships a Training module built around a catalogue: a defined, admin-maintained list of the courses the organisation offers. Staff browse that catalogue and submit a request against a specific course rather than describing training in free text. Once a request is logged, it carries a status through to completion: requested, then accepted, then completed, so there is always one place to check where a given request stands. Because every request points to a catalogue entry rather than a typed description, two requests for “first aid refresher” are provably the same course, not two slightly different write-ups of the same idea.

    This is the step that sits before the reporting and record-keeping covered in the training management system: the request is the intake, the tracker is the ledger.

    What a training request form should capture

    Whether it is built in software or on paper as an interim step, a training request form that will actually hold up under a client or audit review needs:

    • Staff identity: name and a staff or employee identifier, plus department or site, so the request is tied to a specific person in a specific role.
    • Course reference: the exact course name as it appears in the training catalogue, not a free-text description that can drift between requests.
    • Request date: the date the request was raised, independent of when it was actioned.
    • Status: a single current state (requested, accepted, completed) rather than scattered notes about where things stand.
    • Acceptance record: the date the request was accepted and actioned, so the gap between asking and acting is visible.

    Keep the form to those fields. Adding a free-text justification box or a manager sign-off step that the underlying system does not actually enforce creates a form that looks more rigorous than the process behind it.

    Common mistakes to avoid

    A training request form with these mistakes built into it will not hold up under a client or audit review:

    • Treating the request as the same thing as the record. A request is an intake event; completion evidence belongs in the broader training record, not folded into the request itself.
    • Letting requests sit with no status. A request with no visible state is indistinguishable from a request nobody has seen.
    • Free-text course names. If the course is not tied to a catalogue entry, two requests for what should be the same training cannot be matched to each other later.
    • No date on the request itself. Without a request date, there is no way to measure how long a team takes to action training needs, which is often exactly what a client review asks about.

    Frequently asked questions

    Is a training request form the same as a training tracker?

    No. The request form is how a training need enters the system. The tracker is the ongoing record of what was assigned, accepted and completed across the whole team. See the training tracker guide for the record-keeping side.

    What happens after a request is submitted?

    In AVES, a submitted request moves to an accepted status once it is actioned and then through to completed once the training itself has taken place. Each stage is a dated status change, not a separate document.

    Does the request need a manager approval step?

    AVES’s Training module is built around catalogue-based browse, request and accept actions. If your operation needs a formal manager sign-off ahead of that, that approval should happen as a separate, documented step rather than being assumed into the request form itself.

    Can a request be linked to a licence renewal deadline?

    The request record itself tracks dates of request and acceptance. For licence-driven training, pair it with the expiry or next-due marker that a complete training record should carry, covered in the training management system guide.

    Where this fits with the rest of your HR records

    A training request form works best alongside the other documented HR touchpoints security teams already run: performance development plans for ongoing staff development, and employee warning notices for the disciplinary side. Keeping all three on dated, status-tracked records rather than loose paperwork is what makes a client or licensing review straightforward instead of stressful. The same discipline applies to the operational logs your guards keep shift to shift, such as the security guard logbook.

    More templates like this training request form are shared on the AVES Instagram, @avessecurity.

    Book a 30-minute demo and we will show you the actual AVES Training screen, including how a request moves from submitted to accepted to completed. Book a demo, or start a free trial to see the catalogue and request flow for yourself.

  • Asset Tagging Sample: 6 Critical Lifecycle Stages

    Asset Tagging Sample: 6 Critical Lifecycle Stages

    An asset tagging sample is a worked example showing how a single serialised item, such as a two-way radio or CCTV unit, is recorded from the day it enters a security company’s system to the day it is retired, including the fields that change at each stage: onboarding, location, custodian, transfer, stocktake and retirement.

    Most explanations of asset tagging describe the idea in the abstract. What is harder to find is a concrete example: one real asset, followed stage by stage, showing exactly what gets recorded and when. That is what this guide walks through.

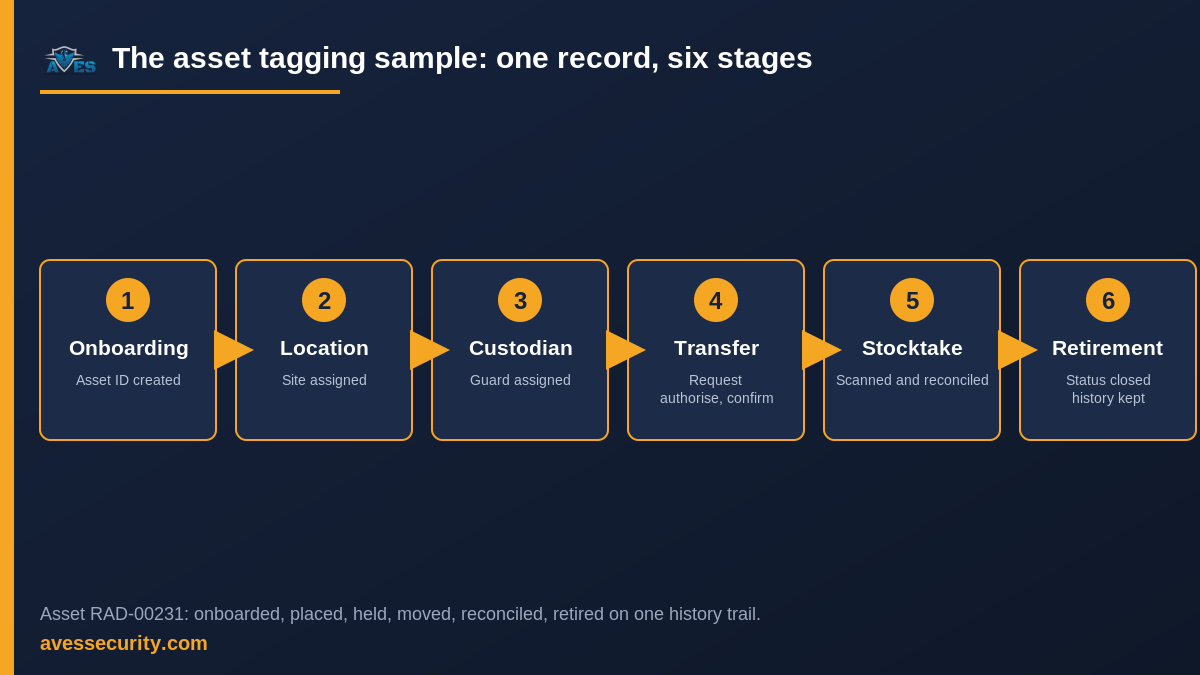
    asset tagging sample lifecycle diagram showing six stages from onboarding to retirement

    Why a worked example matters more than a definition

    Knowing that asset tagging gives an item a unique ID is one thing. Knowing what that ID actually tracks and when the record is supposed to change is another.

    Most mismatches between a tagging system and reality happen at the transitions: the moment an asset moves site, changes hands or goes for repair. A definition will not show you what a transfer record looks like partway through approval, or what a stocktake flags when an item cannot be found. A good asset tagging sample will.

    The asset tagging sample: one radio, tag to retirement

    This asset tagging sample follows a single asset through six real stages, using the asset-code prefix, transfer workflow, custodian field and stocktake process a security company’s assets module actually runs on.

    The asset: a two-way radio, asset code RAD-00231, issued to AVES Protective Services’ Riverside Mall site.

    Stage What happens Field or record updated
    1. Onboarding The radio is received into the system under the organisation’s RAD- asset-code prefix and given a unique ID. Asset ID created, type and description logged
    2. Location placement The radio is assigned to Riverside Mall as its home site. Location field set
    3. Custodian assignment The radio is handed to a named guard for the shift. Custodian field set to that guard
    4. Transfer The site needs an extra radio at a second location. A transfer is requested, authorised by a supervisor and confirmed received at the new site. Transfer logged: requested, authorised, confirmed; location field updated
    5. Stocktake At the next scheduled stocktake, the radio is scanned on site and reconciled against the system record, with no mismatch found. Stocktake entry added, status confirmed
    6. Defect and retirement Months later the radio develops a fault. It is flagged as defective, then moved to under-repair status. After repeated failures it is retired. Status changed to defective, then retired; history trail kept

    Every row above changes a field on the same asset record, not a fresh entry. That is the point of tagging: one scannable ID carries the full history, rather than six disconnected notes in six different places.

    That matters beyond the shift itself. When a client or an insurer later asks where RAD-00231 was on a given date, the full six-stage history can be exported from the one record rather than reconstructed from six separate logs. The same applies when an internal audit needs every asset that passed through a particular site.

    What a good asset tagging sample should always show

    A genuine asset tagging sample, not just a definition, should demonstrate:

    • A unique asset ID tied to one physical item for its whole working life
    • An onboarding step that assigns the ID and basic details at the point the asset is received
    • A location field that updates whenever the asset moves site
    • A named custodian, not just “the site” or “the team”
    • A transfer step with request, authorisation and confirmation, not a single tap
    • A stocktake that reconciles the system record against what is actually scanned
    • A status field that reflects defects and retirement without deleting the asset’s history

    Common mistakes a worked example exposes

    Walking through a real asset tagging sample also exposes the mistakes a bare definition hides:

    Treating the ID as the whole record. The asset code is just the key. The value is in what gets updated against it: location, custodian, status, each time something changes.

    Skipping the authorise step on a transfer. A transfer that only records “requested” and “confirmed” with nothing in between loses the approval trail a dispute would need.

    Letting custodian go stale. If the custodian field is only set once, at onboarding, it stops reflecting who actually has the asset after the first shift change.

    Treating a stocktake as a one-off. A single stocktake catches mismatches that already happened. A scheduled one catches them early, before an item is genuinely lost.

    Deleting a retired asset. Retirement should change the status, not remove the record. Deleting it erases the exact history a later audit would need.

    FAQ

    Is an asset tagging sample the same as an asset tagging template?
    They overlap. A template is usually a blank table of the fields to track. A sample, like the one above, shows those same fields filled in and changing across a real sequence of events.

    How many stages does a typical asset go through?
    It depends on the item. A radio or camera that moves between sites will usually pass through onboarding, location, custodian, transfer and stocktake stages several times before an eventual retirement. The six stages above are the complete set, not a fixed count per asset.

    What happens to the record once an asset is retired?
    The record’s status changes to retired, but the history is not deleted. Keeping the trail intact is what lets a later audit confirm where the item was and who held it, right up to the point it was taken out of service.

    Does every asset need a transfer record?
    Only assets that move between sites or custodians. An item that stays at one location with one custodian for its whole life will show onboarding, custodian and stocktake entries, but no transfer.

    Can a lost asset reappear in the record?
    Yes. If a stocktake cannot locate an item, it is flagged, not deleted. If it is later found, the same record is updated rather than re-created, keeping one continuous history.

    How this looks inside AVES

    AVES’s asset tagging software runs the six-stage pattern above as a working system rather than a worked example: onboarding through the receive endpoint with an organisation’s own asset-code prefix, location placement, custodian assign and release, transfers that move through request, authorise and confirm or reject, scan-to-reconcile stocktakes and status changes through to retirement, all kept on a single asset history trail. For how the four tagging methods behind the ID itself compare, see what is asset tagging.

    An asset tagging sample tracks operational history; it is distinct from the fixed asset register, which is the financial view of what a company owns and from the asset handover form, which logs a single handover event rather than a full lifecycle. The same discipline, tagging and logging every change rather than trusting memory, is also how AVES records daily guard activity in the security guard logbook.

    If your business issues serialised equipment across more than one site, book a 30-minute demo and we will show you the asset tagging sample behind this exact example, onboarding, transfer and stocktake included.

    Book a demo or start a free trial.

    Follow AVES on Instagram for more security operations guidance.

  • Reimbursement Request Form: 7 Critical Fields to Include

    Reimbursement Request Form: 7 Critical Fields to Include

    Security guards and field supervisors spend their own money more often than most employees realise: fuel for a site-to-site run, parking at a client property, a replacement torch battery, a toll on a late callout. None of that gets paid back fairly unless the claim is captured on a form built to survive a payroll review, not scrawled on the back of a receipt. A reimbursement request form is what turns that improvising into a process.

    A reimbursement request form is the document an employee completes to claim back money spent on the company’s behalf. It records what was bought, why, how much and who approved it, so the expense can be verified and added to the employee’s next pay run instead of being paid out ad hoc or disputed after the fact.

    The problem: claims that cannot be checked

    A security company running guards across several sites sees a steady trickle of small, legitimate expenses. The trouble starts when there is no standard way to claim them. One guard texts a photo of a receipt to a supervisor. Another hands over a paper slip at the end of the month. A third simply forgets, then raises it weeks later when the amount is harder to verify.

    Without a consistent form, payroll cannot tell a genuine claim from a guess, cannot check it was actually approved and cannot tie it to a specific pay run with any confidence. That is how claims get paid twice, missed entirely or argued over after the payslip has already gone out.

    Why it matters for a security company

    Guards and supervisors are mobile by the nature of the job: multi-site patrols, gate duty at a client’s premises, emergency callouts outside a normal roster. Out-of-pocket spending is routine, not exceptional, which makes a repeatable claim process a payroll necessity rather than a nice-to-have.

    A proper form also protects the company. A claim with a date, an amount, a reason and a named approver is auditable if a client or an internal review ever asks why a cost was paid. A claim with none of that is just a number someone remembers approving, which is a weak position to be in during any dispute. A consistent reimbursement request form turns routine out-of-pocket spending into a predictable payroll task rather than a monthly argument.

    How it works: from claim to payslip

    The form itself is only half the process. Once an employee submits it, a manager reviews the claim against the stated reason and the evidence attached, then approves or rejects it. An approved claim is not paid as a one-off transaction floating outside the normal pay cycle; it is added to the employee’s next payroll run as a specific line item, so it appears on the payslip alongside wages, overtime and any deductions for that period, with a clear record of which run it landed in.

    That last point matters more than it sounds. A reimbursement that is approved verbally and “sorted out later” tends to either get paid twice because nobody remembers it was already settled, or missed entirely because nobody remembers it at all. Tying every approved claim to a specific run closes both gaps.

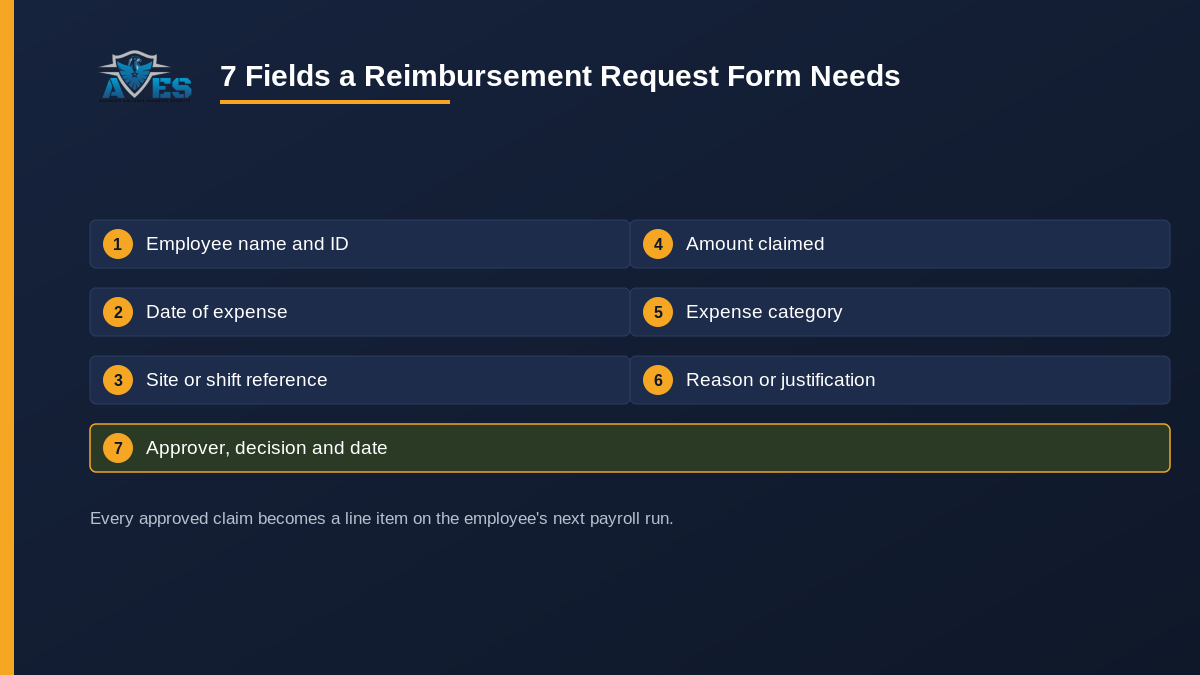
    7 fields a reimbursement request form needs: employee name and ID, date of expense, site or shift reference, amount claimed, expense category, reason, approver decision and date

    7 essential fields a reimbursement request form needs

    1. Employee name and ID. Enough to identify who is claiming without relying on a supervisor’s memory.
    2. Date of expense. The day the money was actually spent, not the day the form was filled in.
    3. Site or shift reference. Which location, client site or shift the expense relates to, so it can be checked against a roster if needed.
    4. Expense category. Fuel, parking, tools, equipment repair, meals on an extended shift and so on. A short fixed list is easier to review than free text.
    5. Amount claimed. The exact figure, in the currency the claim was incurred in if the company operates across borders.
    6. Reason or justification. A short explanation of why the expense was necessary for the job, not just what it was.
    7. Approver name, decision and date. Who reviewed the claim, what they decided and when they decided it, so the claim has a clear audit trail before it ever reaches a pay run.

    A claim missing any of these is harder to defend later. A reimbursement request form with all seven fields is a five-minute approval, not a month-end argument.

    Common mistakes security companies make

    Most of what goes wrong with a reimbursement request form comes down to one of four habits.

    No fixed expense categories. Free-text “what did you buy” fields turn into a mess of inconsistent entries that nobody can total up by type at the end of the quarter.

    Approval happens after the money is already spent and already reimbursed. Verbal approval followed by an informal cash handout removes the audit trail the form exists to create.

    Claims arrive after the payroll run has already closed. A form with no deadline tied to the pay cycle guarantees a backlog of “catch-up” claims that disrupt the next run instead of the one they belonged to.

    Treating reimbursement as a one-off payment instead of a payroll line item. A reimbursement paid outside the normal pay run, by cash or a separate bank transfer, has no paper trail connecting it to a specific payslip, which is exactly the dispute this form is meant to prevent.

    How AVES handles it

    AVES does not treat an approved reimbursement request form as paperwork that happens outside payroll. Once a claim is approved, it is added as a line item to the employee’s next payroll run, the same run that calculates wages, overtime and any deductions for that period, so it shows up on the resulting payslip rather than sitting in an unexplained cash drawer. That keeps the claim tied to one specific pay cycle, which is the detail that stops it being paid twice or forgotten.

    AVES does not replace the claim form itself with a dedicated receipt-scanning app; the fields above are what a company should capture before a claim ever reaches payroll. What AVES is responsible for is making sure that once a claim is approved, it reliably reaches the right pay run and the right payslip.

    FAQ

    Is a reimbursement request form the same as an invoice?

    No. An invoice is a bill one party sends another for goods or services. A reimbursement request form is an internal claim an employee submits to be paid back for money they already spent on the company’s behalf.

    Should reimbursements be paid separately from a wage payment?

    It is cleaner to add an approved reimbursement to the employee’s next scheduled payroll run rather than paying it out as a separate transaction, because that keeps one record, on one payslip, instead of two disconnected payments to track.

    What happens to a claim that is rejected?

    It should be recorded as rejected, with a reason, rather than simply deleted, so there is a record of why it was not paid if the employee queries it later.

    Who should approve reimbursement claims?

    Typically the employee’s direct supervisor or site manager, someone close enough to the work to judge whether the expense was reasonable, before it is passed on to payroll for the next run.

    Does a reimbursement need a receipt?

    Most security companies require some form of proof for anything beyond a trivial amount. A form with no evidence field makes every claim a judgement call on trust alone.

    Where this fits in your payroll loop

    A reimbursement request form is the first step in a chain that runs from a guard’s out-of-pocket spend through to a correctly itemised payslip. The same discipline that keeps a performance development plan or an employee write-up form auditable, a named approver, a date, a clear record, applies here too. On the finance side, the same approved-claim logic is what keeps an accounts receivable ageing report accurate when a client contract passes costs through to billing. If your current process for any of this is still a logbook and a filing cabinet, the same gap shows up in a security guard logbook that nobody can search.

    Book a 30-minute demo and we will show you exactly how an approved reimbursement claim lands on the right payroll run and the right payslip: book a demo. Prefer to explore first? Start a free trial. Follow AVES on Instagram for product updates.

  • What Is Asset Tagging? 4 Methods Security Teams Use

    What Is Asset Tagging? 4 Methods Security Teams Use

    What is asset tagging? It is how security companies keep equipment that moves, CCTV units, two-way radios, body cameras and access-control hardware, accountable instead of letting it drift into a spreadsheet nobody trusts.

    Asset tagging is the practice of giving a physical asset, such as a radio, camera or access-control panel, a unique identifier (a barcode, QR code, RFID tag or serial number) so it can be scanned, located and tracked through its working life, from the day it is issued to the day it is retired.

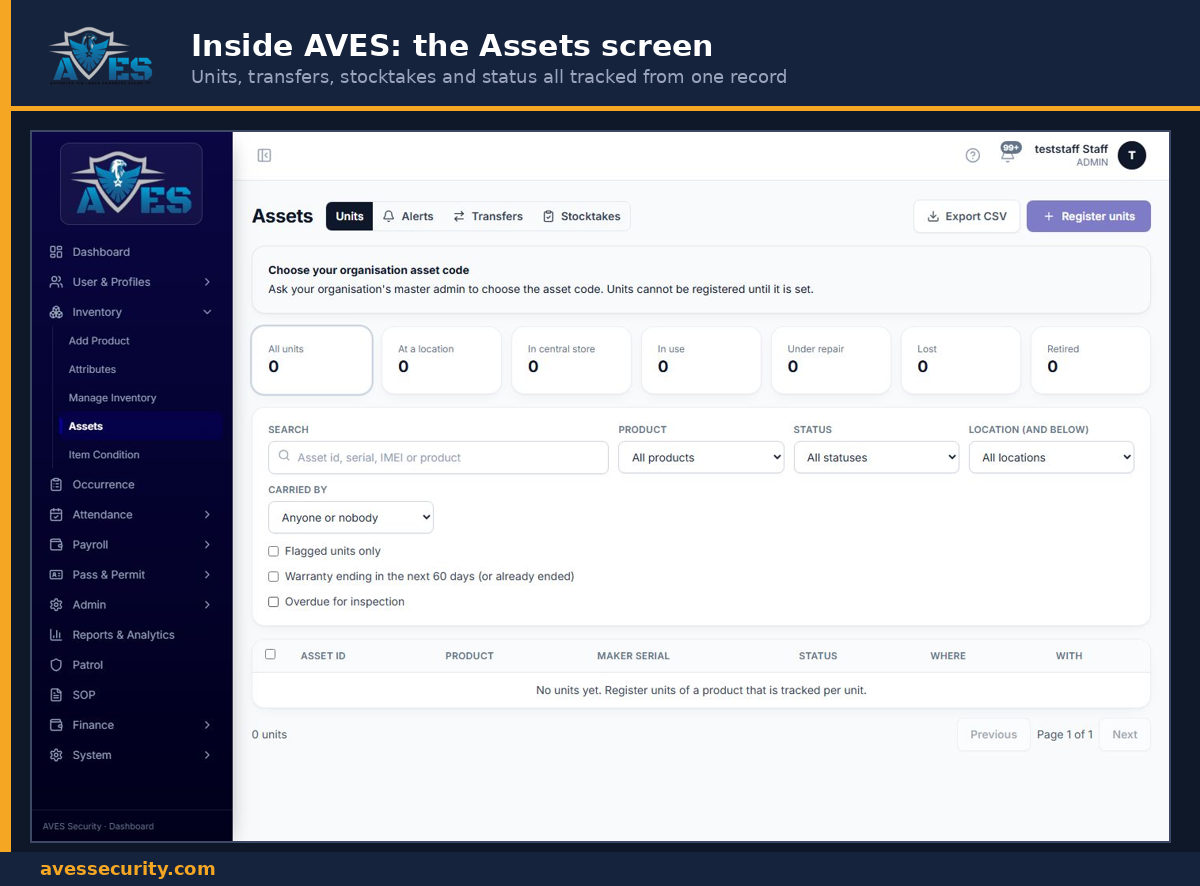
    AVES Assets screen showing units, transfers and stocktakes
    Inside AVES: the Assets screen tracks units, transfers, stocktakes and status from one record.

    The problem: equipment nobody can account for

    Most security companies start tracking equipment on a spreadsheet: one row per item, a column for who has it. It works for a month. Then a guard swaps sites. A supervisor hands a radio to a replacement without logging it. A stocktake turns up three missing units nobody can explain. A spreadsheet does not update itself when equipment moves, and if nobody scans anything the record and the reality drift apart.

    Asset tagging closes that gap by attaching the identifier directly to the physical item, so every scan, not every memory, updates the record.

    Why asset tagging matters for a security company

    Understanding what is asset tagging is only useful once it is tied back to day-to-day operations.

    A security contract depends on equipment being where it is supposed to be. A missing radio during a shift is a safety gap, not just a cost. Disputed handovers (who had the camera last, who lost the key) waste management time and damage trust between guards and supervisors. A stocktake that relies on manual counting can take a full day; one built on scanning tagged assets can take an hour.

    Tagging also creates an audit trail. When a client or an insurer asks where a serialised item was on a given date, a tagged asset has a scannable history. An untagged one has a guess.

    How asset tagging works: 4 common methods

    Barcode labels

    A printed barcode sticker is applied to the asset and scanned with a phone or handheld scanner. Cheap and durable, but line of sight is needed to read it.

    QR codes

    A QR code holds more information than a barcode and can be scanned reliably with any smartphone camera, which is why it has become the standard for field teams who are already carrying a phone during patrols and inspections.

    RFID tags

    A radio-frequency tag can be read without a direct line of sight, which suits bulk scanning (for example, scanning a rack of radios at once) but costs more per tag than barcodes or QR codes.

    Serial number tracking

    Many devices, such as CCTV units, already carry a manufacturer serial number. Recording that number against the asset avoids adding a physical tag at all, though it depends on the serial number staying legible and unique in the system.

    Most security companies use a QR code or barcode for day-to-day scanning and keep the manufacturer serial number as a secondary identifier for warranty and procurement records.

    What a security team should tag and track

    Once the basics of what is asset tagging are clear, the next question is what a workable record needs to capture. At a minimum, it should include:

    • A unique asset ID or tag code, applied once and never reused
    • Asset type and description (for example, radio, CCTV unit or access panel)
    • Current location or site
    • Custodian: who currently holds or is responsible for the asset
    • Status: in use, in storage, under repair or retired
    • Transfer history: when it moved, who authorised the move and who confirmed receipt
    • Condition notes or defect flags, logged at the point they are noticed

    Without most of these fields, a tag is just a sticker. The value comes from what is recorded every time the tag is scanned.

    Common mistakes security teams make with asset tagging

    Even a team that already understands what is asset tagging and why it matters can fall into the same handful of traps.

    Tagging everything, including low-value consumables. Tag what is worth tracking individually, serialised and reissuable equipment, not disposable stock that is better handled as bulk inventory.

    No transfer step between locations. A tag that is scanned on issue but never scanned again on transfer or return gives a false sense of accuracy. The record is only as good as the last scan.

    No named custodian. An asset assigned to “the site” rather than a person makes any later dispute impossible to resolve.

    Retiring an asset by deleting it. Deleting a record erases its history. Retiring it should change its status and keep the trail intact for later reference.

    FAQ

    These are the questions security teams most often ask once they understand what is asset tagging and start planning a rollout.

    Is asset tagging the same as inventory management?
    No. Inventory management typically counts bulk stock. Asset tagging tracks individual, serialised items through their own lifecycle: who has them, where they are and what condition they are in.

    Do I need special hardware to scan tags?
    For barcodes and QR codes, a smartphone camera is enough. RFID tags need a dedicated reader, which is why most field teams default to QR codes.

    How often should tagged assets be stocktaked?
    That depends on how often equipment changes hands. A security company running serialised radios and cameras across multiple sites typically benefits from a scheduled stocktake rather than an ad hoc one, so mismatches surface on a predictable cycle.

    What happens if a tag is lost or damaged?
    The asset record stays intact under its unique ID; a new physical tag can be reissued and linked to the same record so the history is not lost.

    How this looks in practice

    AVES’s assets module applies the same principle described above to a security company’s own equipment. Each serialised item (CCTV units and radios included) gets a unique ID that is scanned during checklists, inspections and stocktakes, with a recorded history of its location, custodian and transfers between sites. Transfers go through a request, authorise and confirm step rather than an informal handoff. A stocktake reconciles what is recorded against what is actually scanned on site. For the full breakdown of what a tagging system should do, see our guide to asset tagging software.

    Asset tagging is also distinct from two related records worth knowing about. The fixed asset register is the financial view of what a company owns. The asset handover form logs a single handover event rather than an asset’s full lifecycle. For equipment issued for a single shift rather than tracked long-term, see our equipment sign out sheet guide. The same discipline of scanning and logging is worth comparing with how AVES records daily guard activity in the security guard logbook.

    The question of what is asset tagging really worth to a growing security business is best answered by seeing it running on real equipment. If your business issues serialised equipment across more than one site, book a 30-minute demo and we will show you the actual asset tagging screen: onboarding, transfers and a scan-to-reconcile stocktake.

    Book a demo or start a free trial.

    Follow AVES on Instagram for more security operations guidance.

  • Visitor Badge Template: 8 Critical Fields to Include

    Visitor Badge Template: 8 Critical Fields to Include

    Author: Nithish, AVES Security content team. Last updated: 14 October 2026.

    A visitor badge template is the set of fields a site prints or displays on every temporary pass it issues, covering who the visitor is, who they are seeing, which areas they can enter and when the badge stops working. A badge with the wrong fields looks official but proves nothing if it is ever questioned.

    Most sites already hand out some kind of visitor badge. Far fewer have actually decided what belongs on it. A sticker with just a name and today’s date looks fine at the front desk, but it cannot answer the questions that matter later: which zones was this person cleared for, who approved the visit and is the badge even still valid.

    This guide covers the eight fields a visitor badge template needs, the mistakes that turn a badge into decoration instead of a control and how AVES issues and verifies badges without a stack of paper at the desk.

    8 fields a visitor badge template needs

    Why a visitor badge template matters

    A badge is the one thing every other person on site sees. If it only shows a name, nobody else can tell at a glance whether this visitor is cleared for the warehouse floor or just the lobby, or whether the badge was issued an hour ago or three days ago. The fields on the badge are what turn it from a sticker into something a guard, an employee or another visitor can actually rely on.

    It also matters after the fact. If a badge is found somewhere it should not be, or a visitor is challenged and cannot produce one, the fields on the template decide how fast that gets resolved. A badge with a visible expiry and a scannable ID gets checked in seconds. One with just a name does not.

    How AVES issues and verifies a visitor badge

    AVES builds the badge from its Security Pass module rather than a printed pad. A visit starts with an access pass request that goes through an approval step, so a badge only exists once someone with the authority to grant it has signed off. The pass carries the visitor’s ID and profile photo, captured at issue rather than copied from an old file.

    Each pass also carries a QR code. A guard at any checkpoint can scan it to pull up the record instantly, including who approved the visit and when the pass expires, instead of trusting whatever is printed on the badge itself. AVES also supports admin-configured colour sets for passes, so a site can assign a visible colour per visitor type or zone and know at a glance which badges belong where, on top of whatever the QR scan confirms.

    The 8 fields a visitor badge template needs

    These are the fields that keep a visitor badge template useful rather than decorative.

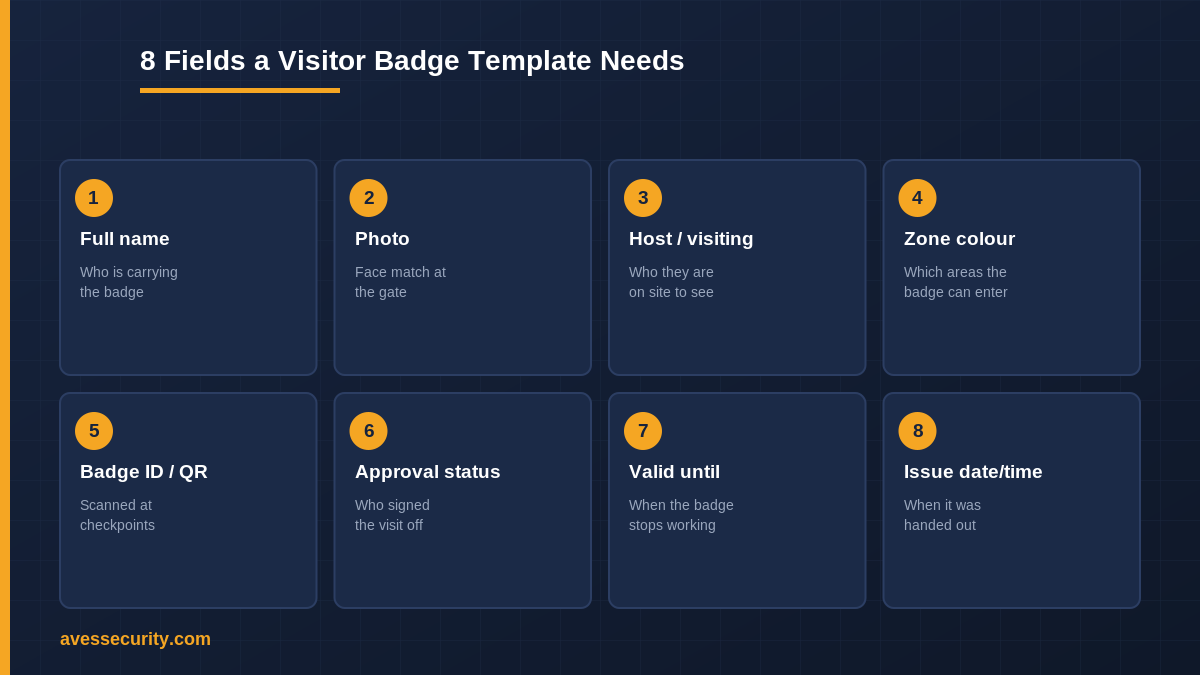
    1. Full name. Printed large enough to read from a few metres away, not just on file somewhere behind the desk.
    2. Photo. A face match a guard can check against the person wearing the badge, captured at issue rather than reused.
    3. Host or reason for visit. Who they are on site to see, so a challenge at any point has an immediate answer.
    4. Zone or colour. Which areas the badge is cleared for, visible at a glance without needing to ask.
    5. Badge ID or QR code. Something a guard can scan at any checkpoint to pull the full record, not just read off the badge.
    6. Approval status. Who signed the visit off, so a badge in circulation always traces back to an approver.
    7. Valid until. A clear expiry, not an open-ended pass that is still technically live a week later.
    8. Issue date and time. When it was handed out, which is what makes a badge found later easy to place.

    A visitor badge template built around those eight fields answers the three questions that actually get asked: who is this, where are they allowed and is the badge still good.

    Common mistakes that make a visitor badge useless

    The most common mistake is no expiry on the badge. Without one, a badge from last month looks exactly like a badge from this morning, and nobody at a glance can tell which is which.

    The second is no photo. A badge with a name but no face match can be handed to anyone, which defeats the point of issuing it to one specific visitor in the first place.

    The third is a badge nobody can scan or verify. If the only way to check a badge is to trust what is printed on it, a guard has no way to catch a badge that was never actually approved.

    The fourth is treating every visitor the same. A contractor heading to a plant room and a guest heading to reception need different zone clearance, and a template with no colour or zone field cannot show the difference.

    How AVES supports this, honestly

    AVES does not print physical badges itself. What it does is manage the pass behind the badge: the approval step, the ID and profile photo capture, the QR code and the admin-configured colour set that a site prints or displays as the badge. Scanning the QR at a checkpoint always shows the live record rather than whatever is printed, which is what keeps an expired or unapproved badge from being trusted on sight.

    There is no automatic door-lock integration tied to badge colour in AVES; zone clearance is something a guard checks against the badge and the scanned record, not something the badge itself enforces at a locked door. Sites that need that level of physical access control should treat the badge as the verification layer, not the lock.

    FAQ

    What is a visitor badge template?

    It is the set of fields a site prints or displays on every visitor badge it issues, covering who the visitor is, who they are seeing, which areas they are cleared for and when the badge expires.

    What fields should a visitor badge include?

    Eight cover most sites: full name, photo, host or reason for visit, zone or colour, badge ID or QR code, approval status, valid until and issue date and time. Fewer than that and a badge usually cannot answer a challenge on its own.

    Does a visitor badge need a photo?

    Yes, for any site that wants the badge to mean something. Without a photo, a badge issued to one visitor can be worn by anyone, which removes the point of issuing it in the first place.

    How is a visitor badge different from a visitor sign in sheet?

    A sign in sheet is the record of who came and went. A badge is what that visitor wears while they are on site, so the two work together rather than replacing each other.

    Does AVES support colour-coded visitor badges?

    Yes. AVES supports admin-configured colour sets for passes, so a site can assign a colour per visitor type or zone and tell badges apart at a glance, alongside the QR scan that confirms the full record.

    Related reading

    See it in action

    Book a 30-minute demo and we will show you how AVES issues, scans and verifies a visitor pass end to end. Book a demo or start a free trial.

    Internal links: Visitor Management System · Visitor Sign In Sheet · Visitor Log Book · Gate Pass Format · Security Incident Log Template (Incident Management hub). External: AVES on Instagram (DoFollow).

  • Security Incident Log Template: 8 Critical Columns to Include

    Security Incident Log Template: 8 Critical Columns to Include

    Author: Kaviarasan, AVES Security content team. Last updated: 13 October 2026.

    A security incident log template is the running register a site uses for every incident it records over time, not a single report. Where an incident report form captures one event in full, the log is the chronological list that lets a supervisor see every entry at a glance: what happened, when, who responded and whether it is closed.

    Most sites already have an incident report form. What a lot of them are missing is the log that sits above it: the single page, book or sheet that lists every incident a site has had this month, in order, so a supervisor does not have to open twenty separate report files to answer “how many incidents did we have in March, and which ones are still open.” That list is the security incident log, and the columns it uses decide whether it is useful six months from now or just a pile of entries nobody can search.

    This guide covers the eight columns a security incident log template needs, the mistakes that turn a log into a liability instead of a record and how AVES replaces the paper version with entries that cannot be rewritten after the fact.

    8 columns a security incident log template needs

    Why a security incident log matters

    A single incident report answers “what happened in this one case.” A log answers a different question: “what has been happening on this site.” Without one, a supervisor handing over to a new shift, briefing a client or preparing for an insurance review has to reconstruct a timeline from loose paperwork, which is slow and easy to get wrong. This is exactly the gap a security incident log template is built to close.

    A proper log also protects the site when something is disputed later. If a client asks whether a particular type of incident has happened before or how many are still open, the answer should be a quick look down one list, not a search through a filing cabinet. And because a log is chronological, it surfaces patterns a single report never will, for example the same location showing up three times in a month, which is a sign worth acting on before it becomes a fourth incident.

    How a security incident log works

    The log itself is simple: one row per incident, added as it happens, never removed. Each row is a short summary, not the full case file. The detail, the photos, the findings, live in the incident report behind it. The log is the index; the report is the record.

    That split in a security incident log template is what makes it fast to scan. A supervisor reviewing a week’s incidents should not have to read eight full reports to get a sense of what happened. They should be able to run down eight rows, spot the one marked still open and go straight to that report. A log that tries to hold the full narrative in every row stops being a log and becomes a duplicate of the report file, which defeats the point.

    The 8 columns a security incident log template needs

    These are the columns that keep a log useful rather than decorative, grounded in how AVES’s incident and safety modules already capture this information.

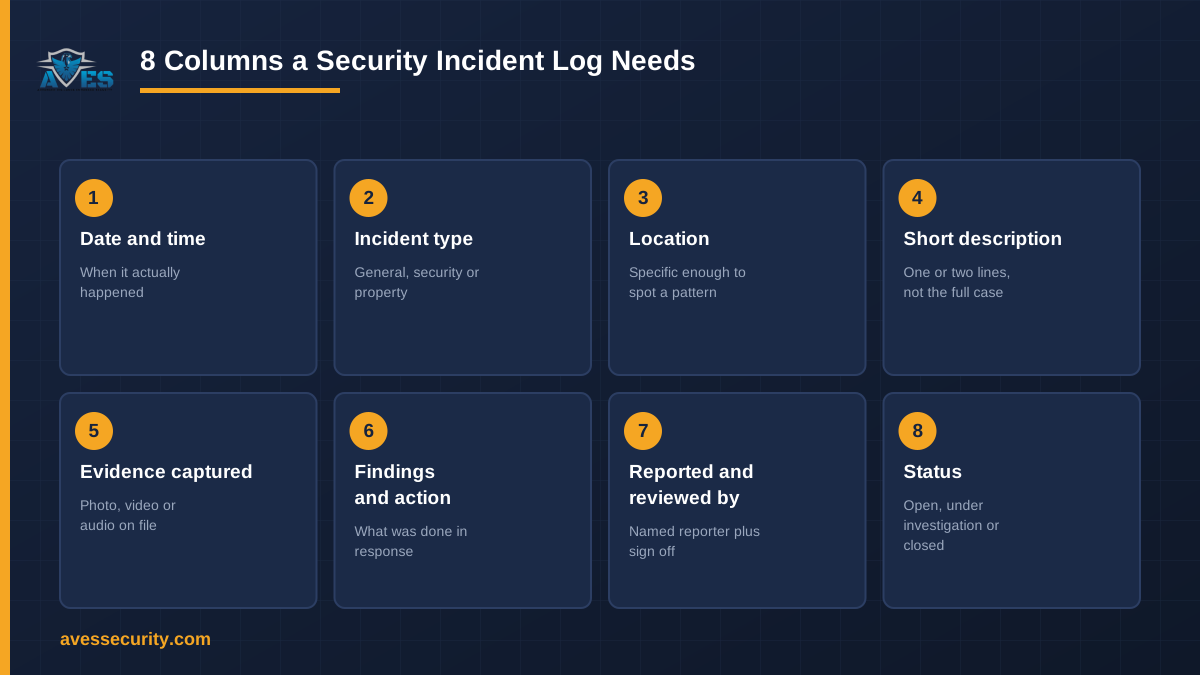
    1. Date and time. When the incident happened, not when it was written up. AVES timestamps every incident, safety and defect entry at the point of submission, so the log reflects the real sequence of events.
    2. Incident type. Whether the entry is a general incident, a security incident or a property/hotel-type event. AVES’s incident forms are split across these categories, which is what lets a log be filtered down to just one type when that is all a reviewer needs.
    3. Location. Where it happened, specific enough to spot a pattern. A log that just says “on site” cannot tell you that the same loading dock has come up three times this quarter.
    4. Short description. One or two lines, enough to know what kind of incident it was without opening the full report. This is the summary row, not the case file.
    5. Evidence captured. Whether photo, video or audio evidence exists for the entry. AVES’s incident forms use a six-sided photo capture alongside video and audio, so the log can show at a glance which entries have supporting evidence and which do not.
    6. Findings and action taken. What was done in response, even as a short note. AVES’s incident and defect/safety forms both carry a findings-and-actions field, which is what a log column should summarise rather than the signature line some paper sheets use instead.
    7. Reported by and reviewed by. Who raised it and who signed it off. AVES ties every incident, safety report and investigation entry to a named reporter, and investigation-type entries carry a separate approvedBy reviewer, so responsibility for both the report and the review is on record.
    8. Status, including whether a police report was filed. Open, under investigation or closed, plus a flag for cases that went to police. AVES’s incident forms carry a police-report field directly, so a log does not need a separate note to show which entries left the building.

    Those eight columns are what turn a list of incidents into something a supervisor can actually use: a column for when, what kind, where, what happened, what evidence exists, what was done, who is accountable and where it stands now.

    Common mistakes that make a security incident log useless

    A security incident log template fails for a handful of predictable reasons. The most common mistake is no status column. Without one, every entry looks permanently unresolved, and a supervisor cannot tell an open case from one that was closed out weeks ago just by looking at the row.

    The second is collapsing the log into the report. Some sites try to write the full narrative into every log row, which makes the log slow to scan and defeats its purpose. The log should point to the report, not replace it.

    The third is no evidence flag. If a log cannot show which entries have supporting photo, video or audio evidence, a reviewer has to open every single report to find out, which is exactly the extra step a log is meant to save.

    The fourth is a paper or shared-spreadsheet log that can be edited after the fact. A row that can be quietly changed is not a record, it is a draft. Entries need to be stamped with who logged them and when, and they need to stay that way once submitted.

    How AVES supports the log, honestly

    AVES does not ship a single standalone “incident log” screen separate from its incident, safety and investigation forms. What it does is capture every incident, defect and investigation entry as a timestamped, named record the moment it is submitted, through the six-sided photo and video and audio evidence capture, a findings-and-actions trail and a police-report field where relevant. Investigation-type entries add a separate approvedBy reviewer on top of the original reporter. That is what any security incident log template in AVES is actually built from.

    That combination, taken together across a site’s incidents, is the log: a chronological, filterable list of every entry, each one backed by its own full report, with nothing in it that can be silently rewritten after submission. There is no signature-image field anywhere in AVES; sign-off is always a named accept, decline or submitted action with a date and time attached, which is a more searchable trail than a scrawl ever was.

    FAQ

    What is a security incident log template?

    It is a running list of every incident a site records, one row per entry, covering when it happened, what kind it was, where, a short description, whether evidence exists, what was done, who is accountable and its current status. It sits above the full incident report rather than replacing it.

    What is the difference between an incident log and an incident report?

    A report captures one incident in full: the narrative, the evidence, the findings. A log is the index across every incident a site has had, built from short summary rows so a supervisor can scan a period at a glance.

    How many columns should a security incident log have?

    Eight is enough for most sites: date and time, incident type, location, short description, evidence flag, findings and action, reported by and reviewed by, plus status. Fewer than that and a log usually loses the ability to show what is still open.

    Can a spreadsheet work as a security incident log?

    It can for a single site with a low incident count, as long as someone actively maintains the status column. It breaks down once entries need to be tied to the original report, once more than one person edits it or once a client or an insurer needs a record that cannot be quietly altered after the fact.

    Does AVES include a police-report field?

    Yes. AVES’s incident forms carry a police-report field alongside the six-sided photo, video and audio evidence capture, so a security incident log template built from these entries can show which incidents went to police without a separate manual note.

    Related reading

    See it in action

    Book a 30-minute demo and we will show you how AVES timestamps and ties together incident, safety and investigation entries so a log always reflects the real record behind it. Book a demo or start a free trial.

    Internal links: Incident Reporting Software · Incident Report Form · Investigation Report Template · Near Miss Report Form · Security Guard Logbook. External: AVES on Instagram (DoFollow).

  • Asset Tagging Software: 7 Critical Features Security Teams Need

    Asset Tagging Software: 7 Critical Features Security Teams Need

    Security companies run on equipment: CCTV units, two-way radios, body cameras, access-control hardware, patrol devices. Asset tagging software is what stops that equipment from becoming a spreadsheet nobody trusts. It gives every item a unique ID, so the business always knows where a piece of equipment is, who has it and what condition it is in.

    Asset tagging software is a system that gives every physical asset, from CCTV units and radios to access-control hardware, a unique ID so it can be scanned, located and tracked through its entire working life: onboarding, placement, transfer, custody and retirement.

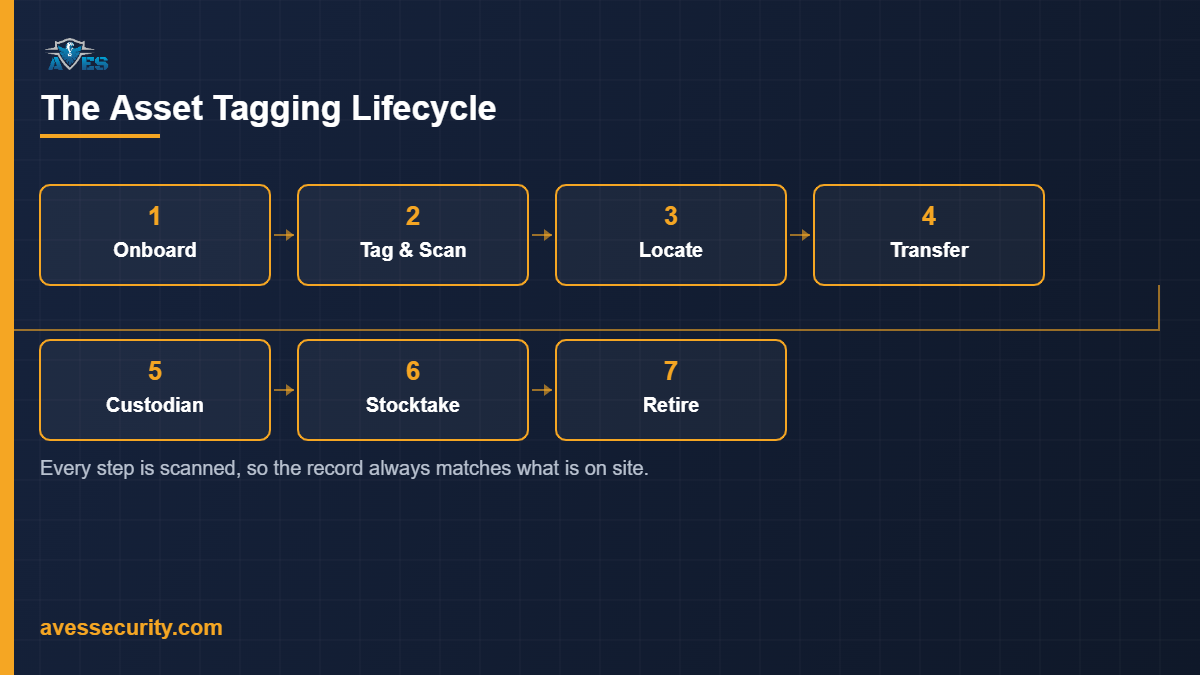
    Diagram of the asset tagging lifecycle: onboard, tag and scan, locate, transfer, assign custodian, stocktake, retire
    The asset tagging lifecycle: every step is scanned, so the record matches what is actually on site.

    The problem with tracking security equipment on a spreadsheet

    Most security companies start with a spreadsheet: one row per radio or camera, a column for who has it. It works for a month. Then a guard swaps sites. A supervisor hands a radio to a replacement without logging it. A stocktake turns up three missing units nobody can explain. The spreadsheet does not update itself when equipment moves. Nobody scans anything, so the record and the reality drift apart.

    For a company running serialised equipment such as CCTV units and radios across multiple sites, that drift is not a minor annoyance. It shows up as lost equipment, disputed handovers and a stocktake that takes a full day of manual counting instead of an hour of scanning.

    Why asset tagging matters for a security company

    A security contract depends on equipment being where it is supposed to be. A missing radio during a shift is a safety gap, not just a cost. Asset tagging software closes that gap by tying every physical item to a record that updates every time the item moves, changes hands or changes status.

    It also protects the business side of the relationship. When equipment is tagged and its location and custodian are logged, a dispute over a lost or damaged item has an audit trail behind it rather than a guess.

    How asset tagging software works

    Each asset is given a unique ID at onboarding, tagged with an organisation-specific asset-code prefix so items from different sites or clients are never confused. From that point, the asset’s ID is scanned during checklists, inspections and stocktakes and every scan adds to a history trail: where the item was, who scanned it and when.

    When an asset needs to change hands or sites, the system runs the move as a request: a transfer is requested, authorised, then confirmed, rejected or cancelled, rather than simply being noted after the fact. A custodian can be assigned to an asset and released when it is handed back, so “who has this right now” is always a lookup, not a phone call.

    7 things asset tagging software must do

    1. Asset onboarding. New equipment is received into the system through a dedicated intake step, with an organisation-specific asset-code prefix applied so codes stay unique across sites and clients.
    2. A unique, scannable ID per asset. Every asset carries one ID that is scanned during checklists and inspections, building a history trail instead of a one-off note.
    3. Location placement. Each asset has a recorded location, so “which site is this radio actually at” is a lookup, not a guess.
    4. Transfers between sites or organisations. Moving an asset is a workflow: request, authorise, then confirm, reject or cancel, so a transfer cannot happen silently.
    5. Custodian assignment and release. An asset can be assigned to a named custodian and released when it is returned, keeping accountability with a person, not just a site.
    6. Physical stocktakes by scanning. A stocktake is run by scanning assets to reconcile what is recorded against what is actually on site, rather than counting by hand.
    7. Status changes, defect flagging and retirement. An asset’s status can be updated, a defect flagged against it and it can be retired from active use, with the change kept on its record. Asset data can also be exported for reporting.

    Common mistakes when tagging security assets

    • Tagging equipment but never scanning it again. A tag with no scanning discipline behind it is just a sticker. The value is in the history trail that builds up every time the asset is scanned during a checklist, inspection or stocktake.
    • Letting transfers happen off the record. If a guard or supervisor can hand equipment to someone else without the system knowing, the custodian field stops meaning anything. Transfers need to go through request and authorisation, not a verbal handover.
    • Treating a stocktake as an annual event. Scan-to-reconcile stocktakes are quick enough to run more often. Waiting a year to find out equipment is missing is waiting too long.
    • Mixing asset codes across sites or clients. Without an organisation-specific prefix, the same-looking code can mean two different items at two different sites, which defeats the point of unique tagging.
    • Not logging the custodian release. Assigning an asset to someone is only half the record. If it is not released when returned, the system still shows it as checked out.

    Frequently asked questions

    Is asset tagging software the same as an asset register?

    No. A fixed asset register (see our fixed asset register guide) is primarily a financial record of what a company owns. Asset tagging software is operational: it tracks where each tagged item physically is, who holds it and its movement history, which then feeds into that register.

    What counts as an asset worth tagging?

    Serialised equipment that a security company issues and reissues is the clearest case: CCTV units, radios and similar hardware that need to be tracked individually rather than counted in bulk.

    Does asset tagging cover a one-off equipment handover?

    A single handover, such as issuing a radio for a shift, is better logged through a handover record (see our asset handover form guide). Asset tagging software is for the ongoing lifecycle of the asset across many handovers, transfers and stocktakes.

    How does a stocktake actually work?

    Assets are scanned against their recorded location, so the stocktake reconciles what should be on site with what is confirmed on site, flagging any mismatch instead of relying on a manual count.

    What happens to an asset’s history when it is retired?

    Retiring an asset updates its status rather than deleting its record, so the onboarding, transfer, custodian and inspection history stays available for later reference.

    Where asset tagging fits in your wider security operations

    Asset tagging software does not replace equipment handed out for a single shift (covered in our equipment sign out sheet guide) or the financial view of what the company owns (the fixed asset register). It sits alongside both, and alongside the wider platform described in our security guard management software overview, as the operational record for equipment that moves between people and sites. The same discipline of scanning and logging that works for assets is worth comparing with how AVES handles daily guard activity in the security guard logbook.

    For product updates, follow AVES Security on Instagram.

    If your business issues serialised equipment across more than one site, book a 30-minute demo and we will show you the actual asset tagging screen: onboarding, transfers and a scan-to-reconcile stocktake.

    Book a demo or start a free trial.