Category: Guides

Foundational guides and explainers on security management.

  • Disciplinary Action Tracking System: Chaos to Strong Proof

    Disciplinary Action Tracking System: Chaos to Strong Proof

    You already know the guard you are thinking about right now.

    Maybe it is a pattern of late arrivals that keeps almost becoming a real conversation. Maybe it is something more serious that happened last month. You are still not sure what got written down about it, or by whom.

    That uncertainty is the real problem. Not the guard, not even the incident itself. It is the fact that when something happens on a security site, the record of it usually lives in someone’s memory, a text message, or a note nobody else will ever see.

    This guide walks through what a real disciplinary action tracking system actually needs to do, where security teams get burned by relying on memory instead and how to build a process that protects your guards and your company at the same time.

    Why Security Teams Struggle With This More Than Most

    Security work has a specific problem that most industries do not deal with the same way. Your people work alone. They work overnight. They work across sites you cannot personally observe on any given shift.

    That means disciplinary issues almost never surface in the moment. They surface later, through a client complaint, an incident report, or a supervisor piecing together what happened after the fact. By the time you are having the conversation, you are already relying on memory to reconstruct something that should have been written down as it happened.

    You are not looking for a lecture about accountability. You already run a tight operation. What you actually need is a way to make sure the second incident gets treated differently than the first, because right now, without a real record, it often does not.

    What a Disciplinary Action Tracking System Is Actually For

    Most security companies think they have a handle on employee conduct until someone asks a specific question they cannot answer with dates and details. A disciplinary action tracking system exists to close exactly that gap. It is not about building a case against your guards, it is about making sure that when an incident happens, the record of it does not live in a supervisor’s memory or a text message nobody else will ever see. Without a real disciplinary action tracking system in place, the second incident often gets treated no differently than the first, simply because there is no documented history connecting the two.

    Strip away the HR language and a disciplinary action tracking system exists to answer one question honestly: if this guard’s conduct ever gets questioned by a client, an insurer, or a lawyer, can you show exactly what happened and what you did about it?

    Without a proper disciplinary action tracking system, disciplinary history lives in scattered memories, texts and private notes nobody else can see. A real disciplinary action tracking system turns that chaos into dated, defensible proof, so the second incident never gets treated like the first.

    Most companies think they can answer that question. Fewer actually can, once someone asks for dates, specifics and who was told what.

    A supervisor’s memory of “we talked to him about it” does not hold up the same way a dated, written record does. The gap between those two things is exactly where a lot of security companies get exposed, usually at the worst possible moment.

    What Belongs in a Real Disciplinary Record

    A disciplinary action tracking system that actually holds up when it matters comes down to a few non negotiable pieces.

    Record the fact, not your interpretation of it.

    “Arrived 40 minutes after shift start, no notice given” holds up. “Guard does not seem to care about the job” does not. The first is defensible. The second is an opinion that can be argued with.

    Separate a first incident from a pattern.

    A single late arrival and a third late arrival in two months are different conversations entirely. A record without dates cannot tell the difference. That distinction is often what determines whether an action is fair.

    Include the guard’s side.

    A one-sided record looks exactly like what people worry disciplinary action tracking system becomes. Documenting what the guard said in response protects everyone, including the company, if the record is ever reviewed later.

    Keep it somewhere every future reviewer can see the same history.

    A note in one supervisor’s private notebook is not a system. If the next supervisor cannot see what already happened, the pattern that should trigger a serious conversation gets missed entirely. It is the same shift away from memory that made a proper guard logbook worth building in the first place.

    Where This Usually Goes Wrong

    Here is the pattern we see most often. It rarely comes from bad intentions.

    A serious incident happens. It gets documented thoroughly, because it is serious enough that someone remembers to treat it like a misconduct documentation system should. A disciplinary action tracking system exists to close exactly that gap. The minor stuff before it, the small lapses that would have shown the pattern, never got written down anywhere. So when the serious incident finally happens, it looks like it came out of nowhere, even though it did not.

    This is not a training problem. It is a threshold problem. Most security teams only document when something feels big enough to matter, which means the smaller signals that actually predict the big thing never make it into any record at all.

    The fix is lowering that threshold, not raising your tolerance for paperwork. A verbal conversation about a minor issue is worth one dated line. It takes thirty seconds and it is the difference between a documented pattern and a memory nobody can prove.

    Being Honest About What AVES Does Today

    AVES includes a confirmed module for this, called Staff Showcause internally, grouped with Training and Performance Development Plan under what the platform calls Internal Security Team Management. It handles disciplinary action tracking system processes with documented HR records.

    Here is what we can say with confidence and what we cannot yet. Training and Performance Development Plan both live inside a Staff Development section of the AVES mobile app. Given how closely Staff Showcause is grouped with those two, it likely lives there as well, functioning as the platform’s own version of an HR disciplinary records software layer. That is a reasonable inference based on the product’s own structure, not a confirmed screen we have walked through ourselves yet.

    What we are not going to do is describe fields, buttons, or steps we have not actually verified. If your business needs a hard commitment on exactly how a disciplinary record gets created in AVES today, ask us directly rather than trusting a guess dressed up as a feature list. That kind of honesty costs us a little polish in a blog post. It is worth more than a feature description that turns out to be wrong the first time someone tries to use it.

    What This Looks Like Once It Is Working

    Six months into a real disciplinary action tracking system process, nothing about it looks dramatic. That is the point.

    Every incident, minor or serious, gets one dated line the same day it happens. Supervisors across every site can see the same history for any guard, not just the ones they personally manage. When a pattern starts forming, someone notices it before it becomes a crisis, because the record makes the pattern visible instead of leaving it scattered across memories that do not talk to each other.

    Nobody is scrambling to reconstruct what happened three months ago when a client or an insurer finally asks. The record already exists, because writing it down was never treated as optional.

    Where to Start This Week

    Pick one site. For the next two weeks, write one dated line for every disciplinary conversation, no matter how small it feels in the moment. Include what happened, what was said to the guard and what the guard said back.

    At the end of two weeks, look at what you have. You will likely see a pattern you did not fully register while it was happening in real time. That is exactly the gap a disciplinary action tracking system is meant to close. It is worth closing before the next serious incident forces the question.

    If you are managing this across several sites and supervisors, keeping every record consistent as part of a real employee conduct tracking tool can start to slip. It is worth talking to us about how AVES’s Staff Showcause module and also disciplinary action tracking software fits into that. We would rather tell you honestly what it does today than oversell it and have you find the gap yourself.

    Building a proper disciplinary action tracking system does not require complicated software or a legal team. It requires consistency: one dated line for every incident, no matter how small it feels in the moment. Security teams that put off setting up a disciplinary action tracking system usually regret it the first time a client, an insurer, or a lawyer asks for proof of what happened and what was done about it. The companies that get this right treat documentation as routine, not reactive, so that when a pattern does emerge, it is visible in the record instead of scattered across memories that were never written down.

    Want to see what a documented disciplinary record actually looks like in practice? Book a walkthrough and we’ll show you.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    Is this really worth building out, or am I overreacting to one bad incident?

    If you have ever had to explain a termination decision after the fact, or defend one, the answer is yes. A documented process costs almost nothing to maintain and protects you the one time it actually matters.

    What if documenting everything makes my supervisors look like they are building a case against people?

    That is a fair concern. It is a framing problem, not a documentation problem. A record that notes both sides of an incident, including what the guard said, reads as fair. A record that only captures the accusation does not. The fix is in how you write it, not whether you write it.

    Do I need software for this, or can I just keep better notes?

    You can absolutely run this on paper if you are consistent about it. Software helps most once you are managing multiple supervisors across multiple sites, where “consistent” starts breaking down without a shared system everyone actually uses.

    What if my current setup already feels fine?

    It usually feels fine right up until someone asks a specific question you cannot answer with dates and details. That is the actual test, not whether anything has gone wrong yet.
  • Role-Based Permissions: Stop Guessing Who Sees What

    Role-Based Permissions: Stop Guessing Who Sees What

    You added a second site. Then a third. Now you run five and something has started to bother you.

    Nobody ever sat down and decided who inside your system should actually be able to do what. Everyone just has an account. You are not being paranoid for wondering if that catches up with you eventually.

    You are the person who has to answer for it if the wrong person opens, edits, or deletes something they should never have touched. That is not a fun position to be in when a client asks how you control access.

    Here is the honest answer and how role-based permissions actually work.

    Why This Starts Feeling Wrong Around Site Three

    At one site, loose access feels fine. You know everyone. You trust them. Nothing has gone wrong yet.

    At five or ten sites, across clients with different confidentiality expectations, that same setup quietly becomes a real problem. Someone edits a record they had no business touching. Nobody planned that. It happened because nobody ever defined what their role should allow in the first place.

    This is exactly what role-based permissions exist to fix. Not because your team did something wrong. Because trust alone does not scale past a certain size and you already know that or you would not be reading this.

    What This Actually Is

    Inside AVES this lives under User & Profiles, in a section called Permissions. A role there is not a vague label like “guard” or “admin.” It is a defined set of what someone can create, view, update, or delete, plus which pages they are even allowed to open.

    Assign a user to that role and they inherit exactly that access. Nothing more, nothing less. This is the foundation of real user role management, not a login screen that only pretends to draw boundaries.

    How Role Creation Actually Works

    Here is the real flow, not a simplified version of it.

    You go to Permissions inside User & Profiles and click Add New Role. Type the role name and click Create Role. The system confirms with “Role Created Successfully.”

    From there you click the edit icon on that role to open module permissions. For every module in the system, you check or uncheck Create, Update, Delete and View. There is a Select All option if a role genuinely needs full access to something, though that should be the exception, not the default.

    Next is the Page Access tab. This is separate from module permissions and it controls something different: which pages the role can open at all. You toggle access on or off for each page. Blue means granted. White means denied.

    Then there is Calendar Page Access. Each calendar item has its own User and Admin access levels, so a supervisor’s calendar view can be configured differently from what a guard sees.

    Click Save and the system confirms with “Permissions updated successfully!” The change takes effect immediately. No delay, no waiting for a sync.

    What Most People Get Wrong Here

    The most common mistake is clicking Select All out of convenience. It feels efficient in the moment. It also quietly recreates the exact unrestricted access problem that proper access control is supposed to solve.

    The second mistake is treating module permissions and Page Access as the same setting. They are not. A role-based permissions can pass one and fail the other if only one of the two tabs gets configured.

    The third is forgetting Calendar Page Access exists entirely, because it lives on its own tab. Save a role after only touching the first two and calendar access does not automatically follow along. You have to set it on purpose.

    The fourth and the one people notice too late, is deleting a role without checking who’s still assigned to it. There is no dependency warning shown in the current build.

    One Honest Quirk Worth Knowing

    Deleting a role is a trash-icon action with a confirmation prompt. That prompt currently reads “Are you sure you want to delete this user?” even though you are deleting a role, not a user.

    That is not something you did wrong. It is simply how the current screen is labeled. Knowing about it ahead of time means it will not throw you off the first time you see it and it is exactly the kind of small, honest detail that separates real product experience from a polished feature description.

    The Trade-Off Nobody Tells You About

    There is no dramatic failure story here and manufacturing one would not be honest.

    The real cost of skipping proper permission management is slow, not sudden. Every day multiple people share loosely defined access, you are relying on memory and good intentions to do a job that a defined role should be doing instead. People forget. People change positions. That is normal and it is exactly why the role structure needs to exist outside anyone’s memory.

    How to Know If You Actually Need This

    If you run one site with a small, close team, you probably do not need to act on this today. Full trust across a small operation is not automatically dangerous.

    The moment you manage multiple sites, or multiple clients with different confidentiality expectations, undefined access stops being a minor gap and starts being a structural one. This is when role-based permissions stop being a nice-to-have and start being close to a requirement.

    Ask yourself one direct question. If a client asked you right now who inside your company can see, edit, or delete their records, could you actually answer with specifics? Or would you be describing an assumption everyone has quietly agreed not to test?

    That question usually tells you everything you need to know about whether your current setup is real access control or just an arrangement nobody has stress-tested yet.

    What Changes After You Set This Up

    Nothing dramatic happens the day you finish configuring roles. That is the point.

    Good role-based permissions are invisible during normal operations. You only notice them the moment someone tries to do something they should not be able to do and gets stopped before it becomes a problem.

    What you gain instead is a specific, demonstrable answer the next time someone asks how access is controlled. When a person changes roles or leaves the company, adjusting or removing their access becomes a defined action on a role, not a scramble to remember every corner of the system they could still reach. That is what real user role-based permissions looks like once it is actually working.

    Where This Leaves You

    You did not start a security company to build a permissions matrix. You started it to protect sites and earn the trust of clients who are paying you to take that seriously.

    Role-based permissions are not a feature to get excited about. They are a feature you need to be quietly confident is set up correctly, for every role, across every site you manage.

    If you want to see the Role-based permissions page and its three tabs in action, a live walkthrough shows you the real screens. Not a sales deck.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    Why does loose access control become a problem as I add more sites?

    At one site, trust-based access feels fine because you know everyone. But across five or ten sites with different client confidentiality expectations, undefined access quietly becomes a structural risk someone can end up editing or viewing records they had no business touching, simply because no one ever defined what their role should allow.

    What does a “role” actually control?

    A role is a defined set of what a user can Create, View, Update, or Delete, plus which pages they’re allowed to open. Assigning a user to a role gives them exactly that access nothing more, nothing less.

    Do changes actually apply right away?

    Yes. Save gives you “Permissions updated successfully!” and it’s live immediately. No sync delay, nothing to wait on.

    Do I even need to bother with this if I’ve only got one site?

    If it’s one site and a tight, trusted team, probably not urgent. But the second you’re juggling multiple sites or clients with different confidentiality expectations, it stops being optional. Good gut-check question: if a client asked you right now who can see, edit, or delete their records, could you actually answer that, or would you just be describing an assumption nobody’s ever tested?

    Is Page Access the same thing as module permissions?

    No and this trips people up. Two different tabs, two different jobs. Module permissions decide what someone can do inside a module. Page Access decides whether they can even open the page in the first place. Set one and skip the other and you’ll end up with a role that half-works.

    What’s the mistake almost everyone makes early on?

    Hitting Select All because it’s faster. It feels harmless in the moment, but that’s basically rebuilding the same free-for-all access problem you were trying to get away from. Save it for the rare role that genuinely needs everything.

  • Witness Statement Form: Smart Steps for Security Operations

    Witness Statement Form: Smart Steps for Security Operations

    Most witness statement forms are useless the moment something actually happens.

    Not because the witness statement form is missing fields. Because it was built by someone sitting at a desk with plenty of time, for a guard who’s going to fill it out with none. A theft. A fight. A fall. An argument that got physical fast. Three people talking over each other and somewhere behind you, a manager already calling asking where the report is.

    If the witness statement form falls apart in that moment, everything built on top of it falls apart too. Names get missed. Nobody notes the time. The handwriting is a mess. Six months later, someone challenges the statement in a disciplinary hearing or in court and half the required fields are just blank.

    You already know this. You’re not here for a definition of what a witness statement is. You want a form that survives contact with a real incident and still holds up when someone comes asking for proof months down the line.

    Why Most Witness Statement Forms Fail Before the Incident Even Happens

    Here’s the thing nobody tells you. A witness statement form doesn’t fail during the incident. It fails long before that, sitting in a folder, looking fine.

    Wide open text boxes. No real structure. Looks tidy on a screen. Falls apart the second a guard is standing in a car park at 11pm trying to remember which detail goes where.

    Most people treat a witness statement form as paperwork. That’s the mistake. Paperwork gets filed and forgotten. Evidence gets scrutinized, picked apart, questioned. If your witness statement form can’t survive that kind of scrutiny, it was never doing its job in the first place.

    You don’t fix a weak witness statement form by adding more fields. You fix it with structure. Every single field on that form should exist because someone, at some point, badly needed that exact piece of information and didn’t have it.

    What the Form Actually Needs to Capture

    A real witness statement form covers two things. Who’s giving the statement and what actually happened.

    Start with identity and background:

    • Full name and alias if applicable
    • NRIC or national ID number
    • Date of birth and age
    • Nationality and race
    • Gender
    • Department and designation
    • Employment number
    • Phone number and address
    • Join date
    • Language spoken and whether an interpreter was used

    That last one matters more than most people think. Say part of your workforce isn’t fluent in the language the report is written in and no interpreter gets logged. That statement can get challenged later on the simple grounds that the person didn’t fully understand what they signed. If you’re running security in Singapore or Malaysia, this isn’t an edge case. Multilingual crews are the default, not the exception.

    Then the incident-specific side:

    • Date and time of incident
    • Type of incident
    • Location
    • Full details of the incident
    • Head of department sign-off
    • Case status, open or closed
    • Assigned team
    • Completion marker

    Notice what most witness statement form templates skip. A structured incident type field. Without it, every report turns into a wall of free text nobody can search or filter or compare six months later. Your management asks how many altercations happened at a site last quarter and you want that answer in seconds. Not a week spent digging through old PDFs.

    The Mistake That Actually Costs Guards Credibility

    Most articles won’t say this plainly, so here it is. The biggest threat to a witness statement form isn’t a missing field. It’s a delayed one.

    Memory fades fast, faster than people want to admit. Eyewitness recall studies show accuracy drops sharply within the first few hours after something happens. A guard filling out the form the next morning, working from memory, isn’t giving you a witness statement anymore. That’s a reconstruction wearing a witness statement’s clothes.

    Think of it like a photograph versus a painting done from memory. The photo isn’t always flattering. It’s accurate though. The painting might look sharper and more composed, but every time it gets redrawn, details shift a little more.

    The fix is boring and practical. The witness statement form has to be fast enough to fill out on the spot. On a phone or a tablet, right after the incident, while the details are still sharp in someone’s head.

    Common Objections and Why They Don’t Hold Up

    If you’re the one deciding whether to overhaul your process, you’re probably running a few worries through your head right now.

    “Our guards aren’t comfortable with digital tools.”

    Fair concern and it used to carry more weight than it does now. Most guards already run their lives off smartphones. A well-built witness statement form with dropdowns and structured fields is easier to fill out under pressure than a blank paper template, because it tells you what comes next instead of leaving you to remember the order yourself.

    “Paper feels safer for legal purposes.”

    It’s actually the opposite. A paper witness statement form can get lost, damaged or quietly altered with zero trace. A digital record with a timestamp and a locked submission is harder to dispute, not easier. If your process still ends in a filing cabinet, that cabinet is your biggest liability. Not your safeguard.

    “We already have a generic incident report. Why bother with a separate witness statement form?”

    An incident report is the site supervisor’s conclusion about what happened. A witness statement is one specific person’s account, in their own words, tied to their identity. Courts, HR panels and insurance adjusters treat these two documents very differently. Merge them into one and you weaken both.

    What Good Witness Statement Form Implementation Looks Like

    Rolling out a proper witness statement form isn’t some massive project. It comes down to a handful of honest decisions.

    Decide who can actually create a statement. In a well-run setup, that’s the reporting guard or the shift supervisor, not just management sitting in an office. The record gets captured in the moment, not reconstructed after the fact.

    Lock the case status field behind real sign-off. A statement moves from open to closed only after a head of department has reviewed it. That one step alone stops the common problem of cases sitting unresolved for weeks with nobody owning them.

    Make interpreter use mandatory to log. Not optional. If someone needed one, that fact needs to sit on the record permanently.

    Keep the details of incident field generous but guided. Give guards room to write freely, but back that freeform text up with the structured fields above so it isn’t floating on its own with nothing to support it.

    The Hidden Costs Nobody Sees Coming

    Two things tend to blindside teams after they’ve been running a weak process for years.

    First is retrieval time. An insurance claim or legal dispute lands months after the fact and now someone has to dig up the original witness statement form. Buried in a paper archive or scattered across old email attachments, that search alone can eat days. A structured digital system with searchable fields turns the same job into a two-minute lookup.

    Second is inconsistency across sites. Without a standard witness statement form, every site supervisor ends up building their own version over time. Fields drift. Some sites capture NRIC, some don’t. Run an audit across multiple locations and this is the first thing that gets flagged.

    Where This Fits Into the Bigger Picture

    A witness statement form doesn’t work in isolation. It’s strongest when it connects to your shift handover records, your incident reporting system and your guard performance data. Keep these pieces separate and someone has to manually cross-reference them by hand, usually under deadline pressure, which is exactly where mistakes creep in.

    That’s the gap AVES Security Management System was built to close. Instead of a standalone paper witness statement form disconnected from everything else, statements live inside the same system as shift logs, incident reports and guard records. A supervisor pulls up an incident and sees the full picture in one place. No chasing four different documents.

    Getting Started Without Blowing Up Your Whole Process

    You don’t need to replace everything overnight. Start with the witness statement form itself. Get the fields right, make interpreter and language capture mandatory, require sign-off before a case can close.

    Once that foundation is solid, connecting it to a broader digital guard management system stops feeling like a leap and starts feeling like the obvious next move.

    Want to see what a properly structured witness statement form looks like inside a real guard management platform? AVES Security walks through exactly this setup, built around the same fields real security operations actually rely on. Head over to avessecurity.com and see how it fits into a complete paperless guard management workflow.

    Frequently Asked Questions

    What is a witness statement form used for in security operations?

    It captures one person’s account of an incident, in their own words, tied to their identity. Used as evidence in hearings, claims and investigations.

    How is a witness statement form different from an incident report?

    An incident report is the supervisor’s summary. A witness statement form is one individual’s direct account, treated as separate evidence.

    What fields should a witness statement form include?

    Identity details like name, NRIC and language spoken, plus incident details like date, time, location, full account and sign-off.

    Why does the interpreter field matter on a witness statement form?

    Without it logged, a statement can be challenged later if the person wasn’t fluent in the language it was written in.

    How soon after an incident should a witness statement form be filled out?

    Right away, ideally on the spot. Memory accuracy drops fast within hours, so next-day statements are closer to guesswork.

    Can a digital witness statement form hold up legally compared to paper?

    Yes, often better. A timestamped digital record is harder to dispute than paper, which can be lost or altered.

    Does AVES include a witness statement form?

    Yes. It sits inside the same platform as shift logs, incident reports and guard records for a full incident picture in one place.

    You don’t need to replace everything overnight. Start with the witness statement form itself. Get the fields right, make interpreter and language capture mandatory, require sign-off before a case can close.

    Once that foundation is solid, connecting it to a broader digital guard management system stops feeling like a leap and starts feeling like the obvious next move.

    Want to see what a properly structured witness statement form looks like inside a real guard management platform? AVES Security walks through exactly this setup, built around the same fields real security operations actually rely on. Head over to avessecurity.com and see how it fits into a complete paperless guard management workflow.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

  • Supplier Management Guide for Companies

    Supplier Management Guide for Companies

    A truck pulls up at the gate. Driver hands over a box, gets a signature, drives off. Nobody writes down what arrived, when or who signed for it. Feels like nothing. Barely worth pausing the shift for.

    Three weeks later a client calls asking where their shipment went. And you realize… nothing was ever actually tracked. Just a chain of handoffs that nobody wrote down.

    If that’s why you’re reading this, you’re not alone and you’re definitely not behind. Most security companies find this gap the same way after something’s already gone wrong, when it’s too late to fix that one incident but not too late to fix everything after it.

    So let’s get into what real supplier management looks like for a security operation, why the gap matters more than people assume and how you close it without dumping extra work on your guards.

    Why Supplier Management Gets Overlooked Until It’s a Problem

    Most security teams treat access control and incident reports as the “real” job. Deliveries? That’s the side task. The thing that gets handled, not managed.

    Understandable, honestly. A driver shows up, drops something, leaves. Doesn’t feel like the kind of moment that needs paperwork the way an incident does.

    But here’s the thing an unlogged delivery is the same gap as an unrecorded key handover. Same gap as an unrecorded shift. If a client disputes what arrived, if something goes missing between the gate and its final stop or an invoice doesn’t line up with what actually showed up, your only defense is a timestamped record with a name on it. Nothing else holds up.

    This is exactly why supplier management deserves to be a real priority, not something bolted on later. Sites with strict receiving windows. Offices that won’t take deliveries outside business hours. Facilities where weekend or holiday drop-offs need extra eyes. These places feel the gap hardest. No system and you’re leaning on a guard’s memory and a driver’s word, months after it happened.

    What You’re Probably Worried About Right Now

    First time looking into supplier management? A few worries are probably sitting in the back of your head, even if you haven’t said them out loud.

    Will this slow my guards down. Is this yet another system to learn. Will people actually use it or will it end up like every other form filled out halfway, then forgotten.

    Fair worries. They deserve real answers, not just reassurance. Doing this right doesn’t mean more work. It means the same handoff your guards already do, just captured in a way that actually holds up months later.

    How Supplier Management Actually Works in Practice

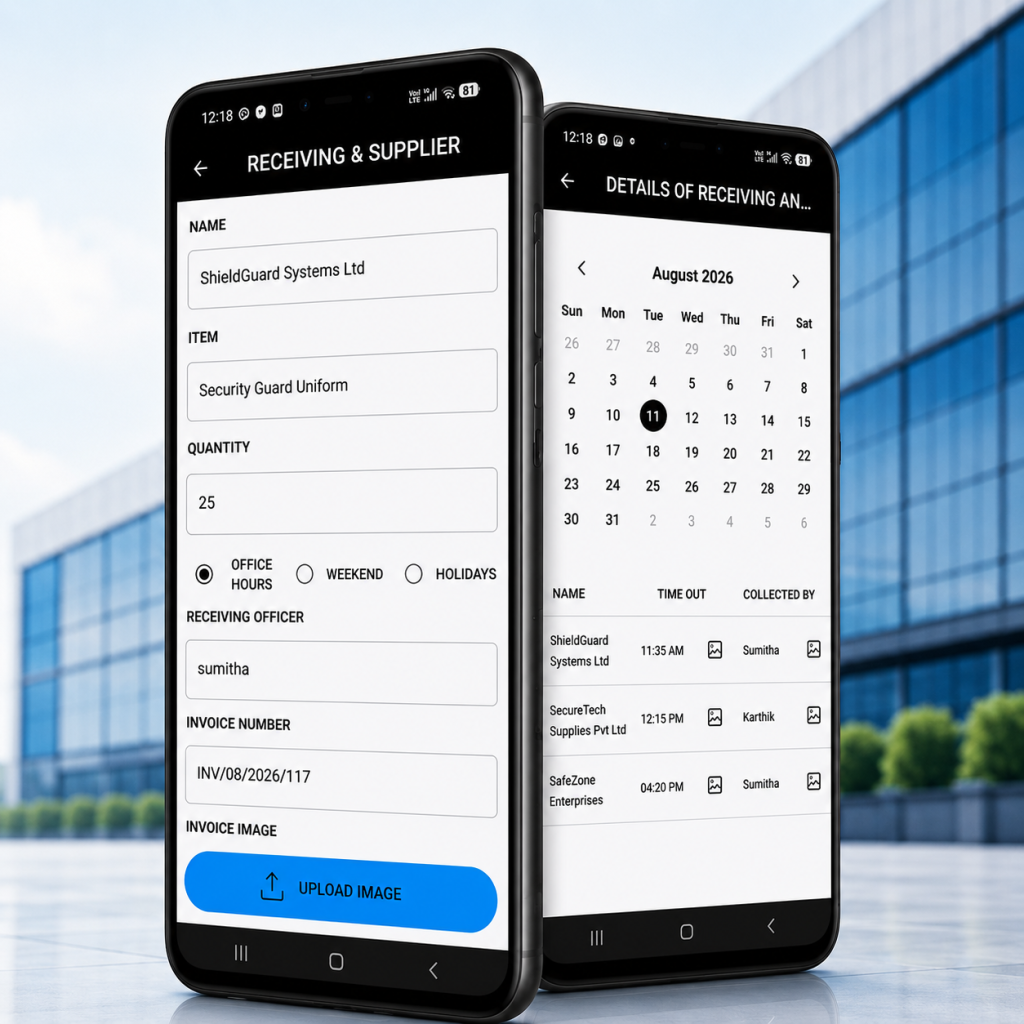
    In AVES, this sits under a module called Receiving Supplier. Two actions, that’s it: Create and Records.

    Create is where a guard logs a delivery as it happens name of the person or company delivering, the item, the quantity and a time-window selector (Office Hours, Weekend, Holidays) so anything unusual gets flagged right away instead of slipping through. The Receiving Officer field fills itself in based on who’s logged into the app, so there’s no guessing later about who actually took the delivery. Add an Invoice Number field and the option to snap a photo of the invoice and that’s the record.

    Records is basically a calendar. Pick a date, see whatever got logged that day. Nothing there? It tells you straight up no data available for the selected date instead of leaving you wondering if the app just broke.

    Think about the difference between a guard’s memory and an actual paper trail. Memory shifts. It softens details, fills gaps without meaning to, changes a little every time it gets retold. A dated record with a name, an invoice number and a photo attached doesn’t do any of that. It just sits there, exactly as it was.

    What Good Supplier Management Doesn’t Include and Why That’s Fine

    Let’s be straight about this, because overselling helps nobody. This is a receiving and delivery log. Not a full vendor management system. No contracts, no purchase orders, no approved supplier lists living in here.

    You won’t find fields for ongoing vendor relationships, payment terms or supplier performance reviews. If your business needs that level of procurement machinery, what you’re getting here is the physical receiving side of things. Not the contractual side.

    Knowing that going in saves you from expecting something that was never meant to be there. Good supplier management, for a security company, means proof of what happened at the gate. Not running your whole purchasing department.

    The Mistakes That Undermine Supplier Management Even When the Tool Is Right

    Having the right tool doesn’t automatically mean good supplier management. The habits around it matter just as much, maybe more.

    Logging the delivery late is probably the most common one. Records pull by date, so an entry made hours later or the next morning, quietly misrepresents when the thing actually showed up. This only works as evidence if the timestamp is real.

    Skipping the invoice photo when there’s one available. Takes a few extra seconds and it’s the first thing that gets dropped when people are busy. Funny enough, it’s also usually the exact piece of paper a dispute ends up hinging on.

    Treating small deliveries like they don’t count. An envelope feels too tiny to log, until it’s the one thing someone’s asking about three weeks from now. Consistency means logging everything. Not just the stuff that feels important at the time.

    Not checking the receiving officer field. It auto-fills based on whoever’s logged in, which sounds convenient until a shared device or a borrowed login quietly puts the wrong name on a delivery.

    And then there’s the big one: treating a verbal handoff like it counts as a record. It doesn’t. If it never made it into the system, as far as your process is concerned, it never happened. Doesn’t matter how well everyone remembers it.

    Building Confidence Before You Commit

    Still on the fence about formalizing this? Here’s the honest trade-off. A little discipline now, a few extra seconds per delivery, buys you real protection later. Almost always a good trade.

    The cost of skipping supplier management shows up when you least expect it. Most weeks, nothing happens and the whole thing feels like overkill. Then one dispute, one missing item, one client asking pointed questions and suddenly the entire investment pays for itself in a single conversation.

    You don’t need to rebuild your whole operation to get here. You need one habit: log the delivery the second it happens. And a system simple enough that your guards actually keep doing it.

    Frequently Asked Questions

    What is supplier management for security companies?


    It means tracking deliveries, vendors and goods received on-site creating a record of what arrived, when and who accepted it, instead of relying on informal handoffs at the gate.

    How does AVES handle supplier management and deliveries?


    Through a Receiving Supplier module with two views: Create, where a guard logs delivery details like item, quantity, time window and invoice and Records, a calendar showing everything logged for a given date.

    Can I attach an invoice to a supplier management record in AVES?


    Yes. The Create form has an Invoice Number field plus the option to upload a photo of the invoice, so the documentation lives right there with the record.

    Does supplier management in AVES flag deliveries outside normal hours?


    Yes the Create form includes a time-window selector for Office Hours, Weekend or Holidays, so your team can categorize and later review anything outside standard hours.

    Is this a full vendor management system?


    No. It logs physical deliveries and receiving details. No contract management, no purchase orders, no ongoing vendor relationship tracking.

    How do I check what was received on a specific day?


    Head to Records. It’s a calendar pick a date and it shows what was logged or tells you plainly if nothing was recorded.

    What to Expect in the First Few Weeks

    Rolling out supplier management for the first time usually goes through a predictable pattern, and knowing it in advance removes a lot of the anxiety.

    Week one feels awkward. Guards forget to log a delivery here and there, not out of resistance, just because it’s a new habit competing with everything else they’re already tracking. This is normal, and it doesn’t mean the system has failed.

    By week three, most teams settle into a rhythm where logging becomes automatic, the same way checking a badge or signing a visitor in became automatic once. The friction that felt real in week one fades once supplier management stops being a new task and becomes just part of how deliveries happen.

    The companies that struggle long-term are usually the ones that gave up in week one, right when the habit was still forming. If you commit to the first month, consistent supplier management tends to take care of itself after that.

    Where This Leaves You

    Supplier management doesn’t have to be complicated and it shouldn’t slow your team down. It just needs to be consistent and it needs to produce a record that actually holds up the day someone questions it.

    AVES keeps it in the same system your guards already use for shifts, incidents and attendance so a delivery record is something you pull up in seconds, invoice photo included, instead of trying to piece it together from a driver’s word weeks later.

    Want to see how AVES handles supplier management and delivery records in practice? You can explore the platform and request a demo at avessecurity.com.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

  • End of Shift, Start of Proof: The Security Daily Activity Report

    End of Shift, Start of Proof: The Security Daily Activity Report

    You already know the feeling

    A client calls asking what happened at the loading dock last Tuesday night.

    You pull the daily activity report. The handwriting is rushed. The times look rounded. Half the details you need were never written down at all.

    Now you are reconstructing a shift from memory, three weeks late, with a client waiting on the other end of the phone.

    If you run a security company or manage guard operations, this is not a hypothetical. It is the exact moment that separates teams who look competent under pressure from teams who look like they are guessing.

    This guide exists to fix that moment before it happens again.

    What a security daily activity report actually is

    A daily activity report, often shortened to DAR, is the document a guard completes at the end of a shift covering everything that happened on site.

    It is different from the two documents people usually confuse it with.

    • Daily briefing happens before the shift starts. It is forward looking. What to watch for today.
    • Occurrence log or incident report captures a specific event the moment it happens. It is narrow by design.
    • Daily activity report is written at the end of the shift and covers the whole picture. Patrols completed. Visitor and gate activity. Equipment condition. Incidents referenced. Site status at handover.

    A shift with zero incidents still needs a complete daily activity report, because the report is not only for when something goes wrong. It is the record that nothing did, which is exactly what a paying client wants confirmed.

    Why most daily activity reports fail before they are even read

    Here is what almost nobody tells you when you start standardizing this process.

    The failure point is rarely the format of the form. It is when the form gets filled out.

    A guard who writes the daily activity report from memory at the end of a twelve hour shift is not lying. They are compressing eight hours of small details into ten rushed minutes and details get smoothed over without anyone intending it.

    That creates three problems you will eventually run into if you have not already.

    Problem one: inconsistent handwriting and formatting. A daily activity report from one guard is unreadable next to a daily activity report from another. The moment a client asks you to compare coverage across a week, you are translating five different handwriting styles into one story.

    Problem two: no proof of when it was written. A supervisor cannot tell if a report was logged in real time or backfilled the next morning right before you asked for it.

    Problem three: a missed round is invisible until it matters. If a patrol never happened and nobody wrote it down, the paper looks identical to a shift where everything went right.

    None of this means the daily activity report is a broken idea. It means paper was never built to prove anything. It was only ever built to record.

    The five sections every security daily activity report actually needs

    Strip away the site specific extras and a usable daily activity report breaks into five parts, in the order a shift naturally happens.

    1. Shift and post details

    Guard name, date, shift hours, post or account assigned. This ties the report to a specific roster entry so nobody has to guess who was where.

    2. Equipment and inventory

    Radio, keys, access cards issued and returned. Vehicle condition if applicable. Any equipment fault noted at the start or end of the shift.

    3. Activity timeline

    Patrols run and when. Gate and visitor movements. Deliveries received. Logged as it happens, not reconstructed at the end.

    4. Incidents and exceptions

    A reference to anything already logged in the incident report or occurrence log during the shift, so the two documents tell the same story instead of two different ones.

    5. Handover status

    Site condition at the end of shift. Anything flagged for the incoming guard. Keys and equipment counted back in.

    If you are building your own format from scratch, resist the urge to make it exhaustive. A one page report that gets filled in consistently every single time beats a three page one that gets rushed in the last ten minutes of a shift.

    The mistake most security companies make here

    Most teams try to fix the daily activity report problem by making the checklist stricter. More boxes. More signatures. More rules about penmanship.

    That almost never works. Here is the part nobody tells you upfront.

    A stricter form does not change when a guard sits down to fill it out. It just makes the rushed version longer.

    The actual fix is changing where the information comes from in the first place.

    If your patrols are already being logged with a timestamp. If your incident reports already capture photos and video the moment something happens. If your shift handover is already recorded digitally. Then the daily activity report stops being something a guard writes from memory. It becomes something that gets assembled from data that already exists.

    That is the shift worth making. It is a smaller change than most operators expect.

    What this looks like in practice

    This is where AVES fits into the daily activity report picture. I want to be direct about what it does and does not do, because vague claims help nobody.

    AVES is cloud based security management software used across residential, corporate, healthcare, manufacturing and warehousing sites. Guards use the mobile app to log activity as the shift happens rather than at the end of it.

    The checklist module timestamps every entry automatically, so a completed round and a skipped one no longer look the same on paper.

    The reports module lets guards submit incident reports in real time with photos and video attached, instead of a written description pieced together hours later.

    The shift module handles shift handover and shift requests digitally, so the handover step, the one guards skip first under pressure, has a record either way.

    Every action is timestamped and stored, which is what makes an audit ready PDF report possible on demand instead of a scramble through binders when a client calls.

    Worth knowing before you commit to any platform, including this one. AVES offers limited offline capability, meaning core field actions sync once connectivity returns, but full functionality needs an internet connection. If your sites have serious connectivity gaps, ask any vendor directly how they handle that, not just AVES.

    That kind of honesty is exactly what should decide which platform you trust, not which one has the flashiest demo.

    The real cost of getting this wrong

    Consider the actual math for a moment.

    A mid sized security team spends roughly eight to twelve hours a week on paperwork tasks that a proper system finishes in minutes, based on what similar operators report. At a modest hourly rate, that is real money spent shuffling paper instead of managing risk.

    Now add the cost you cannot put a number on. The client who loses confidence in your security daily activity report because your reporting looked disorganized during an audit. The insurance claim that gets questioned because your incident timeline does not match your daily activity report.

    Paper feels free until the day it costs you a contract.

    How to actually start

    You do not need to overhaul your entire operation this week.

    Start with the five sections above and pick one week to run them consistently across every guard, on paper or digitally, whichever you are using now.

    Then look for the gaps. Missing timestamps. Inconsistent handwriting. Reports that read suspiciously similar every single day, which usually means they are being filled in from habit rather than from what actually happened.

    Once you see exactly where paper is failing you, the decision to move to a digital system stops being a leap of faith. It becomes the obvious next step, because you will already know precisely what problem you are solving.

    If you want to see how AVES handles daily activity reporting alongside patrols, incidents and shift handover in one platform, you can request a demo at avessecurity.com and walk through it with your own sites in mind.

    Frequently Asked Questions

    Does every shift need a full security daily activity report, even a quiet one?

    Yes. A quiet shift with a complete daily activity report is proof nothing went wrong. A quiet shift with no daily activity report is just an assumption.

    How is a security daily activity report different from an occurrence log?

    The occurrence log only captures specific incidents as they happen. The daily activity report covers the entire shift, including the fact that nothing unusual occurred. It should reference any occurrence log entries rather than repeat them.

    Who should read the security daily activity report besides the supervisor?

    Clients often want daily activity reports on a weekly or monthly basis for their own compliance records. Insurers may request them directly after an incident. Treat every daily activity report as something a stranger might eventually read with no other context.

    What is the biggest mistake first time operators make with daily activity reports?

    Making the form longer instead of fixing when it gets filled out. A guard rushing through a five page report at the end of a twelve hour shift will produce worse data than a guard filling out one page as the shift happens.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

  • Stop Missing Parcels: Parcel Tracking Software For Security

    Stop Missing Parcels: Parcel Tracking Software For Security

    Something happened last week and you still do not have a straight answer.

    A parcel came in. A guard signed for it. Now the vendor says it was never delivered. Nobody can prove otherwise.

    If that sounds familiar, you already understand why parcel tracking software for security exists. It is why so many sites are finally moving away from the clipboard. You are not looking for a nice-to-have feature. You are looking for proof, because proof is what stops a dispute from becoming your problem.

    Why This Keeps Happening

    Most sites still handle deliveries the same way they did fifteen years ago. A clipboard by the front desk. A signature that nobody can read. A note scribbled in a margin.

    That system worked when nobody questioned it. It stops working the moment a client, a vendor, or a resident asks where their package went and expects a real answer.

    This is exactly the gap that parcel tracking software for security was built to close. Not to replace your guards, but to give them a system that remembers what a busy shift cannot.

    Without parcel tracking software for security, every delivery dispute becomes a memory contest instead of a records check. Memory rarely holds up well under pressure.

    What You Are Actually Trying to Solve

    You are not trying to buy software for the sake of having software. You are trying to solve a specific fear.

    The fear that one day a client will ask “what happened to this delivery” and your only answer will be a shrug.

    Delivery logging software for security exists to remove that fear. It turns a guard’s memory into a timestamped record that holds up when someone pushes back.

    Here is what most teams do not realize until it is too late. The problem is rarely the missing package itself. The problem is not having any way to prove what happened to it. A five dollar item and a five thousand dollar item cause the exact same headache if there is no record either way, which is exactly why parcel tracking software for security treats every package the same, no matter how small.

    The Honest Trade-Off Nobody Talks About

    Adding any new system means asking your guards to do one more thing during a shift that is already full. That is a real cost. Pretending otherwise would not be honest.

    But compare that cost to the alternative. Right now, every dispute your team faces gets resolved by whoever argues more convincingly, not by what actually happened. Courier tracking for site security exists specifically to take that guesswork out of the equation.

    The teams who get the most value from parcel tracking software for security are not the ones with the fanciest setup. They are the ones who commit to logging every parcel, not just the ones that look important.

    Skipping small items feels harmless in the moment. It is exactly how the gap that parcel tracking software for security is meant to close quietly reopens.

    Three Moments Every Parcel Passes Through

    Whatever system you choose, three moments matter more than anything else.

    Receipt:

    The exact moment a package arrives and a guard accepts it on the site’s behalf.

    Storage:

    Where that package sits and who is responsible for it while it waits for pickup.

    Handover:

    Proof of exactly who received it and when.

    Miss any one of these three moments and you are back to relying on memory. Cover all three and you have parcel receipt and handover records that settle a dispute in minutes instead of days.

    This is the core promise behind parcel tracking software for security. It is not about adding paperwork. It is about making sure receipt, storage and handover are never left to a single person’s recollection.

    What Beginners Get Wrong

    The most common mistake is treating this as an all-or-nothing decision. Teams assume they need parcel tracking software for security to run perfectly from day one or the whole thing is pointless.

    That is not true. It is not how good security operations actually work. Start by logging the deliveries you are already worried about, then expand from there once your guards are comfortable with the habit.

    The second mistake is assuming a verbal handoff is good enough for small items. It is not. The value of chain of custody security guard software comes from consistency, not from judgment calls about what counts as important enough to log.

    A third mistake, often overlooked, is choosing a general delivery app instead of parcel tracking software for security built specifically around how a guard’s shift actually works. General tools are not designed around handover confirmation or site-level custody. That gap shows up exactly when you need it least.

    Why This Protects You, Not Just the Client

    It is easy to think of parcel logging as something you do for the client’s peace of mind. That is only half the picture.

    This is the part of parcel tracking software for security that clients rarely think about. A documented handover also protects your own team. If a package genuinely was handed off correctly, a clean record proves it. Without one, your guards are defending themselves with nothing but their word against a client’s frustration.

    This is the quiet reason experienced security operators take delivery logging software for security seriously long before a client ever demands it. It protects the company as much as it protects the customer.

    Think about the last time a dispute dragged on for days because nobody could point to a record. Parcel tracking software for security exists to make that specific scenario disappear.

    What Good Actually Looks Like

    You do not need a complicated rollout of parcel tracking software for security to get this right. You need consistency.

    Every parcel gets logged the same way, every time, regardless of size or apparent importance. Every handover gets confirmed, not assumed. Every record stays searchable, so a question from three weeks ago can be answered in under a minute instead of an afternoon of guessing.

    That is what parcel tracking software for security is actually supposed to deliver. Not complexity. Clarity, at the exact moment someone asks a hard question.

    Good parcel tracking software for security should feel invisible on a normal day and indispensable on the one day something goes wrong. If it only helps during a crisis, it was not built for daily use. Your guards will quietly stop using it.

    How This Fits Into the Bigger Picture

    Parcel tracking software for security rarely does its job in isolation. It sits alongside gate movement, supplier deliveries and visitor access, all of which touch the same basic question. Who came in, what did they bring and what happened to it.

    If your site already tracks vehicle and material movement at the gate, adding parcel receipt and handover records is a natural next step, not a separate project. The two work together to close the same liability gap from different angles.

    Parcel tracking software for security is strongest when it connects to the rest of your site’s records rather than sitting off on its own as a disconnected log nobody remembers to check.

    Making the Decision Without the Guesswork

    You do not need to overhaul your entire operation this week to benefit from parcel tracking software for security. You need one honest look at your current process and one honest question.

    If a client asked you right now where a specific delivery from two weeks ago ended up, could you answer in five minutes?

    If the answer is no, that is not a failure. It is simply the gap that courier tracking for site security is designed to close. It is a gap every growing security team eventually has to deal with.

    Ask the same question a different way. If a dispute landed on your desk tomorrow, would parcel tracking software for security already have the answer waiting, or would you be starting from zero?

    The Next Step

    You already know the cost of getting this wrong. A disputed delivery, an unhappy client and a guard left defending a decision they cannot fully explain.

    Closing that gap does not require a complicated system. It requires parcel tracking software for security built specifically for how security teams actually operate, not a generic delivery app repurposed for the job.

    If that sounds like the missing piece in your current setup, it is worth seeing how parcel tracking software for security works before your next disputed delivery forces the question.

    A missing parcel is a five-minute problem only if you logged it. Without proof, it’s a week of finger-pointing nobody wins.

    See how parcel tracking software for security closes the gap – before your next disputed delivery does it for you. Book a walkthrough

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    What is parcel tracking software for security, really?

    It’s basically a way to stop relying on memory. Someone signs for a package, someone puts it somewhere, someone hands it off eventually and this just writes all of that down as it happens instead of hoping everyone remembers later.

    Isn’t a sign-in sheet basically the same thing?

    Not really, no. A sheet tells you a box showed up. It doesn’t tell you where it went after that or who actually handed it over. That gap is where most disputes live.

    Does this replace the paper log completely, or run alongside it?

    Replace it. There’s no reason to keep two systems going. The paper one just ends up in a drawer nobody checks anyway.

    Who’s this really protecting, us or the client?

    Both, honestly. The client gets peace of mind that their delivery was handled right. Your team gets something to point to when someone comes in hot with a complaint that isn’t actually your fault.

  • Security Guard Performance Management Guide

    Security Guard Performance Management Guide

    A security guard performance review is not supposed to feel like a trip to the dentist. But that’s exactly how most security company owners run it. They dig up a dusty generic template, scribble a couple of half-hearted notes, sign the bottom and shove it in a filing cabinet for the next twelve months. That lazy habit is the actual reason your turnover keeps climbing.

    Here’s what that officer actually deals with. Twelve hours alone at a client site. Aggressive visitors at the gate. Access control. A 2 a.m. alarm going off with nobody around to back them up. And then you hand them a review that says “good job.” That’s it. That tells them nobody’s watching, nobody cares. Good guards pick up on that fast and they don’t stick around, they go find a company that treats them like it matters. If you want a security guard performance review process that actually works, forget the corporate HR playbook. Look at what the job really involves.

    Why traditional appraisals fail security teams

    Most evaluation templates were built for someone sitting at a desk under office lights. It’s a bit like scoring a race car driver on typing speed, the metrics just don’t apply. A perimeter fence or a lobby desk doesn’t behave like a cubicle. Judge a mobile patrol officer with corporate benchmarks and the whole security guard performance review feels fake before you’ve even asked the first question.

    Guards know within a minute whether you understand their job. If you don’t, they check out mentally right there and good luck getting honest engagement after that. It kills your credibility as a manager instantly. A strong security guard performance review keeps good people, because it’s built around what the work actually looks like, not what a handbook says it should look like.

    Most managers just inherited whatever system was already in place. Annual check-ins, because that’s tradition. But security isn’t an industry where you can afford to wait a year. One missed patrol turns into a break-in or a client walking away entirely. By the time the annual review comes around, bad habits are already baked in and your best officers have already mentally quit.

    The core framework of a security guard performance review

    A real security guard performance review or security guard evaluation, sticks to objective, observable behavior. You can’t grade someone’s vibe or general attitude. You grade what they actually did. A solid framework captures daily reliability and how someone handles a crisis, in equal measure.

    Start with operational reliability: punctuality at shift handover and how strictly someone follows post relief protocol. A guard who shows up ten minutes late forces the outgoing officer to stay late too and that quietly poisons morale across the whole roster. Let tardiness slide long enough and it becomes the norm and your most reliable people start to resent it.

    Next comes tour execution. Are your guards actually hitting checkpoint scans on schedule or are they pencil-whipping the log from inside the guard shack? Patrol integrity is what your client contract is built on. Skip checkpoints and the client is paying for protection they’re not getting.

    You also need to look at incident documentation, meaning how fast and how accurately reports get filed. A report riddled with spelling errors and missing timestamps can wreck your legal standing the moment a case goes to court. Round out your security guard performance review with professional conduct: uniform, grooming and how officers actually talk to clients and visitors.

    Tracking the guard performance metrics that matter

    A real security guard performance review runs on numbers you can actually track week over week, not vague advice about working harder. One of the most important security guard KPIs to start with is tour completion rate. Anything below ninety-five percent on scheduled checkpoint scans and you’ve got a problem worth investigating.

    Incident response time matters too. How long does it take an officer to acknowledge an alarm or check out something suspicious on the property? When someone unauthorized is already inside, minutes are the whole ballgame.

    Report accuracy is another one worth watching, specifically how often a supervisor sends a report back for corrections. If your supervisor’s spending half their morning rewriting other people’s paperwork, that’s not a discipline issue, that’s a training gap that needs fixing.

    Numbers strip out the bias. Nobody can argue with a system showing they missed twelve checkpoints last Tuesday, that’s just what happened. It turns what used to be a tense, emotional conversation into a coaching session grounded in fact. Officers trust a security guard performance review built on data a lot more than one built on whatever mood their supervisor happened to be in.

    Ditching the paper trail for digital tracking

    Paperwork slows everything down and eventually something gets lost. Try running a security guard performance review across dozens of officers using logbooks and scattered spreadsheets and watch how fast the whole system collapses. A dedicated platform removes that headache entirely. Every hour spent digging through last month’s attendance sheet is an hour that should’ve gone toward training or client calls.

    Paper gets coffee stains. It gets left in a glove compartment. It disappears into a filing cabinet somewhere and never resurfaces. Digital tracking keeps everything tied to the right officer’s profile from day one, no exceptions. Cutting the physical logbook out of the process turns admin work from a scavenger hunt into something manageable.

    Walk through the life cycle of a typical paper incident report. An officer scrawls it on a clipboard mid-shift. Hands it to the supervisor at change of shift. It gets tossed into a folder in the back of a patrol car. Weeks go by. Eventually it lands on someone’s desk back at the office and now an assistant’s squinting at bad handwriting trying to figure out what actually happened. By the time management sees it, the incident’s already two weeks old. A digital system just deletes that whole broken chain.

    How AVES Security Management changes the game

    Bring everything into one place and the whole equation changes. AVES Security Management System builds your security guard performance review process, scheduling and incident reporting into a single platform. Inside the performance module, managers log employee periods and departments in a matter of seconds. Pick the name, set the development period, that’s it. No spreadsheet juggling required.

    Supervisors get a structured space to log development goals and flag concerns instead of hunting through a filing cabinet for last month’s notes. You set an agreed improvement action and a clear success measure directly inside the app. Reviews stop being that once-a-year panic because the notes are already there, logged continuously as the year goes on.

    Once daily activity connects directly to long-term development tracking, the culture around here starts to shift. With a proper security guard performance review system in place, supervisors aren’t guessing what happened three months ago anymore. They open the profile, look at real completion numbers and have an honest conversation backed by actual data instead of fuzzy memory.

    Setting goals that actually change behavior

    A security officer performance plan without a deadline attached to each goal is just a wish. Target start and end dates give remedial training or a promotion track, an actual timeline to work against. The AVES calendar lets you set exact dates for any goal in a couple of taps. Officer struggling with report writing? Give them thirty days and pair it with focused training in the app.

    Measurable success criteria tell you, plainly, whether the error rate actually dropped over that window. Continuous feedback, tracked through the calendar, means notes get logged as things happen rather than everyone scrambling to remember details once a year. Real growth comes from small, steady corrections, not one giant overhaul once every twelve months.

    Tell someone to “be more professional” and you’ve told them nothing useful. Tell them “complete every checkpoint scan within ten minutes for the next thirty days” and now there’s an actual target. That’s the difference between vague advice and something a person can actually act on.

    Overcoming pushback from field supervisors

    Roll out a new security guard performance review system and somebody’s going to push back, usually a supervisor claiming they don’t have time for more paperwork. Fair enough, honestly, paperwork pulls them away from the site. Moving to digital cuts that friction down to almost nothing since entry takes seconds, not an afternoon. Officer skepticism around the review process fades too once it’s tied to metrics instead of whatever mood a supervisor’s in that day.

    Trust in the security guard performance review process comes from transparency.. When officers see their completion rate connecting directly to actual career growth, accountability just becomes part of how things work, not a rule being forced on them. Supervisors stop acting like enforcers and start acting like mentors who actually want their people to do well.

    Getting veteran supervisors on board really comes down to showing them the upside. Once they realize a review takes five minutes on a phone instead of a weekend buried in paper, most of the resistance just disappears on its own.

    Your next move

    A proper security guard performance review process turns your security team from a line-item cost into your biggest asset. Pair clear expectations with digital tracking and the administrative mess across your organization starts to clear up on its own. Stop relying on messy paperwork and habits that were never built for this job in the first place. Streamline your performance tracking and build a stronger team with the AVES Security Management System.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

  • Unplanned Events, Real Risk: Event Security Coordination

    Unplanned Events, Real Risk: Event Security Coordination

    You get the call on a Tuesday. A VIP is coming next week. Or someone books a private function for Saturday night, out of nowhere. Or a client tacks a gathering onto the calendar nobody planned for.

    There’s a specific stomach drop that comes with that call. Your regular schedule wasn’t built for this. You know it immediately.

    If you’ve felt that particular mix of pressure and “wait, how do we actually handle this,” you already get why event security coordination matters more than most people admit, at least until something goes wrong once.

    The Fear Nobody Says Out Loud

    Here’s the part nobody puts in the client proposal. It’s not really the event you’re afraid of. It’s what happens if you get it wrong while a client is watching closely.

    A scuffle at the door. A VIP standing around with no clear escort because nobody claimed that job. A parking mess that turns the entrance into chaos before the event starts.

    None of that is really about the event itself. It’s about you and your company. That’s the actual weight event security coordination carries, even though on paper it sounds like nothing more than a scheduling task.

    Why Your Normal Setup Falls Apart Here

    Day to day, your operation runs on routine. Fixed patrols. Predictable shifts. Guards who know the site so well they don’t think about it anymore.

    An event blows all of that up. More people you don’t recognize. A schedule that looks nothing like a normal Tuesday. A client whose reputation is tangled up with yours for a few hours whether either of you likes it or not.

    Without event security coordination, teams end up improvising on the fly. Someone scrambles for extra guards at the last minute. Nobody’s totally sure who’s actually responsible for the VIP’s arrival. The parking plan, if you can call it that, lives buried in a group text somewhere.

    What You’re Probably Wondering, If This Is New To You

    If you’ve never had to coordinate security for an event before, here’s the honest question underneath everything else. Can you pull this off without something slipping through?

    Fair question. Most teams learn event security coordination the hard way, usually after one event where a detail nobody thought to plan for showed up unannounced.

    The good news is the details that matter aren’t some mystery. They show up the same way basically every time. Once you know what they are, this stops feeling like guesswork.

    Not Every Event Needs the Same Level of Fuss

    Something most guides skip. Treating a private birthday party the same as a VIP visit wastes effort exactly where you can’t afford to waste it.

    Event security coordination works better when events get sorted by risk first. A VIP event usually needs its own dedicated incharge and tighter coordination, which is really what VIP event security planning comes down to at its core. A private function might just need standard coverage and a confirmed headcount. Private function security planning rarely needs to go further than that. A regular event sits somewhere between the two.

    Sorting things this way is really the whole trick behind good event security coordination. You spend your best planning energy on what actually needs it, instead of applying the same heavy process to every booking.

    The Four Things That Actually Matter

    You don’t need a complicated system for this. You need four things nailed down for every event security coordination effort, no exceptions.

    Who’s in charge. A named security incharge. One person, accountable start to finish. Not a rotating cast of guards with no clear owner. Getting the security incharge assignment right saves you from a dozen small confusions later.

    Roughly how many people. Even a rough headcount changes staffing, parking allocation and entry point coverage.

    Where the cars go. Event parking isn’t the same as daily traffic. Sort it out ahead of time or deal with chaos at the gate.

    What guards need to know first. A briefing built for this specific event, not a generic one, so your team understands what’s different before it starts. Solid event safety briefing management separates a guard who’s ready from one who’s just showing up.

    Skip more than one of these and event security coordination quietly falls apart right when it matters most.

    What Beginners Get Wrong (And Honestly, It’s Not Their Fault)

    The most common mistake is treating event planning like an extension of the regular schedule instead of its own thing. A guard pulled off routine patrol and dropped into an unfamiliar VIP event with no real briefing is set up to miss things.

    That’s not a skill problem. It’s a planning gap. Event security coordination fails quietly when it gets bolted onto the existing roster as an afterthought instead of getting treated like its own step.

    Mistake two, sneaky one this, is letting event details scatter across messages, emails and random phone calls. By the time the event starts, nobody has the full picture.

    There’s a third one that trips up even experienced teams. Short notice events get treated as lower stakes because there’s less time to plan. Backwards, actually. Short notice makes event security coordination more important, not less.

    The Trade-Off Nobody Loves Talking About

    Planning ahead costs time your team doesn’t always have, especially when notice is short. That’s a real cost.

    But weigh it against the alternative. A poorly coordinated event creates problems that take way longer to clean up afterward, both logistically and with the client relationship itself. Event security coordination that happens even a day in advance beats zero planning every single time.

    The teams that get the most out of this aren’t running some elaborate process. They’re the ones who consistently nail the basics, incharge, headcount, parking, briefing, every time, no matter how small the event looks.

    Why This Protects the Relationship, Not Just the Event

    Clients remember how an event felt, not just whether nothing blew up. That distinction matters more than most security teams give it credit for.

    A team with a parking plan ready, briefed staff who know their role and one clear person running the show looks like a company that’s got this handled. A team scrambling through logistics on the day looks like the opposite, even when nothing goes wrong.

    Event security coordination is what turns “we handled it” into “they really had it handled.” Clients notice that difference even when they can’t quite explain why.

    How This Connects To Everything Else You’re Already Doing

    Events don’t happen in a vacuum away from the rest of your security operation. They tie into shift scheduling, patrol coverage and guest access all at once.

    Event security coordination works best as something your team checks alongside the regular schedule, not as a separate silo where an event can quietly overlap with duties nobody remembered to reroute. Keeping it connected is what actually makes event security coordination reliable week over week.

    Making The Call Without Guessing

    You don’t need to overhaul anything this week to get this right. Just one habit. Capture the basics for every event before it starts instead of piecing them together once guests are already walking through the door.

    Ask yourself something simple about your next booked event. If someone asked right now who’s responsible, roughly how many guests to expect and whether guards have actually been briefed, could you answer without hesitating?

    If the honest answer is no, that’s the exact gap event security coordination is meant to close. It’s a small habit, but it pays for itself the first time a client asks a hard question mid-event.

    The Next Step

    You already know what’s riding on this. A client’s trust. A guard’s ability to do their job well. Your company’s reputation next time someone books an event.

    Closing that gap doesn’t mean reinventing how you run your operation. It means building event security coordination around how events actually unfold, not stretching a generic scheduling tool to cover a job it was never built for. That’s all good event security coordination has ever needed to be.

    If your current process still runs on memory and last-minute texts, event security coordination is worth fixing before the next VIP visit forces the question for you.

    No coordination, no proof it was ever handled well.See how event security coordination keeps every detail covered. Book a walkthrough

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    What’s event security coordination even mean in plain terms?

    Someone owns the event. That’s it, really. Not five people half-responsible. One person, plus the basics sorted before anyone walks in.

    We just throw more guards at events. Isn’t that enough?

    Nope and I get why people think that. More bodies doesn’t help if nobody’s actually running point. I’ve seen four guards standing around an entrance with zero coordination between them.

    Do we really need this? We maybe do two events a year.

    Kind of the opposite logic applies here honestly. Rare events are the ones that catch people off guard, precisely because nobody’s done it enough times to have a rhythm.

    Do VIP events need more attention than a regular one?

    Definitely. VIP stuff usually needs its own dedicated incharge and tighter coordination. A smaller private function can often get by with standard coverage and a decent headcount.

    How does planning ahead actually help the client relationship?

    Clients remember how the event felt more than whether something technically went wrong. A team that clearly has it together, parking sorted, staff briefed, one person running things, just reads as more trustworthy.

  • Visitor Pass Tracking: Closing the Loop on Unreturned Badges

    Visitor Pass Tracking: Closing the Loop on Unreturned Badges

    You’ve probably had this moment. A visitor badge from three weeks ago turns up in someone’s car, still active, still able to open a door it shouldn’t. Nobody remembers issuing it, nobody remembers taking it back.

    That’s not a rare glitch. It’s what happens when temporary access lives on a sign-in sheet instead of a system built to close the loop. If a pass can be issued but never formally returned, it isn’t access control. It’s a gap with a clipboard attached to it.

    This guide walks through what actually breaks down with informal visitor tracking, what real visitor and security pass management should look like instead and how to evaluate a tool without paying for features you’ll never use.

    Why Most Sites Lose Track of Temporary Access

    Most security teams don’t get burned by a bad actor walking in the front door. They get burned by a legitimate pass that was never properly closed out.

    A sign-in book, a spreadsheet, or a stack of laminated badges works fine on a quiet day. It falls apart the moment two supervisors issue passes on the same shift without checking each other’s records. That’s exactly the coordination problem security and visitor pass management is built to solve.

    Real security and visitor pass management isn’t about greeting people at the door. It’s about the full lifecycle of a credential: who issued it, how long it’s valid and confirmation that it came back. Buyers who go shopping for a broad visitor-experience platform with kiosks and host notifications often overpay for features that have nothing to do with the actual liability risk, which is an unreturned credential still sitting active somewhere.

    The Real Risk Isn’t the Visitor, It’s the Unreturned Pass

    Here’s the part most guides skip. The dangerous moment isn’t when a visitor walks in. It’s the moment their access should have expired and didn’t.

    Common failure points we see on sites without structured security and visitor pass management:

    • Passes issued verbally with no record of the validity window
    • No single log showing which credentials are still active right now
    • A returned badge that never gets marked as returned in any system
    • Different supervisors issuing access with no shared visibility

    None of these are visitor problems. They’re record-keeping problems. A tool built for temporary access card management closes this gap by tying every credential to a start time, an end time and a confirmed return, so nothing stays active by accident.

    If you’re worried tightening this process will slow down legitimate visitors or contractors, it usually does the opposite. A guard who can issue and log a pass in under a minute moves faster than one flipping through a paper binder looking for the last entry.

    What Good Visitor and Security Pass Management Actually Covers

    Strip away the sales language and real visitor and security pass management does three things well.

    Any platform claiming to handle visitor and security pass management should be judged against these three steps, not against how polished its sign-in screen looks.

    First, it issues a credential with a defined validity period. Not an open-ended badge that works forever until someone remembers to deactivate it, but a pass scoped to exactly how long that person needs to be on site.

    Second, it tracks the credential while it’s active. A supervisor should be able to see, at a glance, every temporary pass currently valid on the property, not reconstruct that list from memory when a client asks. This is where guest pass tracking software earns its place over a paper log.

    Third, it confirms the return. The credential isn’t closed out because a shift ended. It’s closed out because someone recorded that the badge came back. That confirmation step is what separates visitor and security pass management from a sign-in sheet with extra steps.

    Systems built around unauthorized access prevention software principles treat that third step as non-negotiable, because an unreturned credential is functionally the same risk as a stolen key.

    Hidden Considerations Buyers Discover Too Late

    A few things people usually find out after they’ve already committed to a tool.

    Validity windows matter more than the badge itself. A pass without a hard expiry is a liability that renews itself every day nobody notices it. Ask any vendor directly how visitor pass validity tracking actually works, not just whether the feature exists on a slide.

    Integration with your gate and occurrence records matters. If visitor and security pass management lives in a separate system from your gate logs and occurrence reports, you end up piecing together three records instead of reading one clear picture during a client review.

    Not every “visitor management” tool is scoped the way you need. A lot of platforms in this space are built for corporate lobbies and photo capture, not for a security operation that needs credential issuance, validity and return tracked as one connected record. Ask to see the actual pass lifecycle on a live demo before assuming it fits.

    How to Evaluate a security and visitor Pass Management Tool

    You don’t need the flashiest kiosk on the market. You need a system that closes the loop every single time, which is the actual promise of visitor and security pass management, not just a nicer badge printer.

    A few practical filters worth running any visitor and security pass management platform through:

    • Does every pass get a defined validity window at the moment it’s issued?
    • Can a supervisor see all currently active passes in one place, in real time?
    • Is there a confirmed return step, not just an assumed one?
    • Does it connect to your existing gate and occurrence records, or sit alone?
    • Can the vendor show the actual issuance and return screens live, not in a slide deck?

    If a vendor answers all five clearly, you’re looking at real visitor and security pass management, not a repackaged lobby app wearing a security label.

    Quick Answers Before You Decide

    Do I need visitor and security pass management if my site rarely has visitors? Probably not on day one. But the moment more than one supervisor issues access, informal tracking becomes the risk, not the visitors themselves.

    Is visitor and security pass management the same as a general visitor management system? Not quite. A general visitor management system is often built around lobby check-in and host notifications. Visitor and security pass management is scoped to the credential itself: issuance, validity and confirmed return.

    What’s the single biggest risk this replaces? An active pass nobody remembers issuing. That’s the exact gap unauthorized access prevention software and structured visitor pass validity tracking are designed to close.

    Who Actually Needs This and When

    Not every property needs a full visitor and security pass management platform on day one and that’s worth saying plainly instead of pushing every site toward the same solution. A single-site operation with low visitor traffic can sometimes get by longer on manual tracking than a multi-tenant building or a construction site with rotating contractors.

    The trigger point is usually simple. The moment more than one supervisor can issue a pass, or more than one shift overlaps with active visitors, informal tracking stops working. That’s exactly when visitor and security pass management earns its cost, because the risk isn’t the volume of visitors, it’s the number of people who could issue access without checking a shared record first.

    Sites that delay this decision usually don’t regret the switch. They regret how long they waited, usually after a client audit or an incident forces the question. Building visitor and security pass management into your process before that happens is cheaper than explaining an unreturned credential afterward.

    Where This Leaves You

    None of this requires a complicated rollout. It requires treating every temporary credential as a record with a start, a defined window and a confirmed end, instead of trusting memory to close the loop.

    You already suspect the sign-in sheet isn’t enough. The real question is whether your next system for visitor and security pass management actually tracks the full lifecycle of a pass, or just makes issuing one look more official.

    If you want to see how real visitor and security pass management works end to end, live, on an actual device, that’s a fifteen-minute conversation, not a sales pitch.

    A badge that looks official isn’t the same as access that’s actually controlled.

    See how a real pass gets tracked from issue to return, live. Book a walkthrough.

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    What is visitor and security pass management?

    It’s the process of issuing, tracking and closing out temporary access credentials for visitors, contractors, or short-term staff. It covers three things: who got access, how long it was valid for and whether the credential was confirmed returned.

    Isn’t this the same thing as a visitor management system?

    Not really, no. Most visitor management systems are built around the check-in moment, taking a photo, printing a badge, pinging the host that someone’s arrived. Pass management cares less about the arrival and more about what happens after, whether that badge ever comes back.

    How does the validity window actually work in practice?

    Every pass gets a start point and an end point when it’s created. Once that window closes, it’s expired, full stop, regardless of whether the physical badge made its way back to a drawer yet.

    How’s this different from a Gate Pass?

    Gate Pass is about vehicles and materials crossing in and out. This is about people. They sound similar, they even sit near each other in the product, but they’re solving two different problems and one doesn’t cover the other automatically.

    What’s the mistake companies make most with this?

    Thinking a good-looking badge means access is under control. A laminated pass with no expiry and no return check is really just a nicer paper sign-in sheet, it just feels more official.

  • Pocket Book: From Forgotten Notes to Permanent Proof

    Pocket Book: From Forgotten Notes to Permanent Proof

    A guard notices something worth remembering. A gate that sticks. A visitor who seemed off. A reminder for whoever takes over the post next.

    Where does that note actually go? Half the time, nowhere useful. A scrap of paper on a desk, a text to a supervisor that gets buried, a mental note that’s gone by the next shift.

    This is the small, unglamorous problem Pocket Book is built to solve. Not incidents, not formal reports. Just the ordinary notes that keep a site running smoothly when they’re written down and quietly cause confusion when they’re not.

    What Pocket Book Actually Is

    Pocket Book lives inside AVES under Logs & Reference, right next to SOP. Where SOP holds your uploaded documents and procedures. The tool holds the shorter, dated notes guards and managers log day to day.

    It’s not an incident report. It’s not an occurrence log. Think of Pocket Book as a proper electronic guard logbook, the digital version of the notebook a guard used to carry, minus the part where that notebook gets lost, left in a shack, or scribbled in handwriting nobody can read a month later.

    Some companies still call this kind of tool an e-pocketbook for guards, which is a fitting description. It’s personal, it’s quick to use and it’s meant to be checked constantly, not opened once a week.

    How Creating an Entry Actually Works

    Here’s exactly what the Pocket Book create flow looks like, based on the real screens, not a guess.

    From the Home dashboard, scroll to the Logs & Reference section and tap Pocket Books. From there, tap Create.

    The form asks for three things. A Date, picked from a calendar. A Time, picked from a clock selector. And a Message field, where the actual note goes.

    Fill those in and tap Submit. That’s the entire entry process. No categories to choose, no severity level, no extra fields to slow a guard down mid-shift.

    That simplicity is worth noting on purpose. A digital guard logbook that takes thirty seconds to fill out gets used. One that takes five minutes gets skipped, especially at 3am on a slow night when logging a small observation doesn’t feel urgent enough to justify the effort.

    How Reviewing Past Entries Actually Works

    Tap Records from that screen and you land on a screen titled Details of Pocket Book. It opens to a full month calendar, with today’s date already selected by default.

    Two things stand out here. First, the calendar lets you move month to month using the arrows on either side of the month name, so pulling up an entry from six weeks ago is a couple of taps, not a search through a notebook.

    Second, there’s a toggle above the results labeled My Books and Staff Books. My Books shows entries the current user logged. Staff Books shows entries logged by staff. Switching between them is one tap.

    If there’s nothing logged for the date you’ve selected, the screen tells you so, though it’s worth knowing the exact wording differs slightly depending on which toggle you’re on. My Books shows “No Data Available.” Staff Books shows “No Data available for the Selected Date.” Small inconsistency, but worth knowing so you’re not confused wondering if it means something different.

    Why the “My Books vs Staff Books” Split Matters More Than It Looks

    It’s easy to check one Pocket Book toggle, see nothing logged and assume there’s nothing to see. That’s the most common way this feature gets misread.

    My Books and Staff Books are genuinely separate views. A supervisor checking only My Books on a given date could easily miss entries their team logged under Staff Books for that same day. If you’re reviewing a date for any real reason, check both toggles, not just one.

    What’s Confirmed and What Isn’t Yet

    Being straightforward here matters more than sounding polished. The Pocket Book create and records flows above are confirmed directly from real screens. That part isn’t a guess.

    What isn’t shown anywhere in the current screens: whether a Pocket Book entry can be edited or deleted after it’s submitted, what exactly determines whose entries show up under Staff Books and whether the Message field has any length limit.

    If those details matter for how your team plans to use it, the honest answer is to ask for a live walkthrough of those specific flows before assuming how they work.

    Why This Beats a Handwritten Logbook

    If your team is still using paper, the case for Pocket Book as a way to replace handwritten security logbook habits comes down to four things paper can’t do well. A digital record can’t be torn out. It can’t go missing with the notebook. It timestamps automatically instead of relying on a guard’s memory of when something happened. And it’s searchable by date instead of flipped through page by page.

    None of that requires guards to change what they actually write. It changes what happens to the note after it’s written, which is usually where paper systems fail first.

    Getting the Most Out of Pocket Book

    Keep each entry to one note. A message field that turns into a running list of five unrelated observations is harder to scan later than five separate entries would be.

    Log things close to when they happen, not at the end of a shift from memory. The Date and Time fields exist for a reason.

    Check both toggles when reviewing a date for anything that actually matters. It takes one extra tap and avoids the most common way Pocket Book gets misread.

    What This Actually Looks Like Across a Real Shift

    A day shift guard notices the loading dock gate isn’t latching. Not incident-worthy, but worth the next shift knowing. They open Pocket Book, tap Create and log it in under a minute.

    That entry exists whether or not the guard mentions it verbally at handover. The night guard can check Records, filter to today’s date and see it under My Books if they logged it, or Staff Books if a supervisor is reviewing the whole team’s notes.

    This is where the two toggles in Pocket Book earn their place. A guard cares about their own notes. A supervisor cares about the wider picture. Same tool, two different views.

    Picture a slower shift too, nothing worth a formal report. On paper, that shift often produces nothing written down, since nothing felt urgent enough to bother. With Pocket Book, the bar is lower. A visitor who lingered too long. A flickering light. None of it’s an incident, but all of it becomes searchable history instead of a memory that fades.

    That’s really the point. One entry rarely matters. A pattern across two weeks, the same gate mentioned three times, is what a supervisor only catches if the notes exist somewhere searchable. Scattered notebooks can’t show that. A calendar can.

    Guards who know their Pocket Book notes get reviewed tend to write better ones. No complicated rollout needed, just the habit and a supervisor who actually checks.

    Where to Go From Here

    If your team is still relying on scrap paper or memory for the small stuff, that’s exactly the gap Pocket Book is built to close. Simple entry, simple review, one place instead of scattered notes nobody can find later.

    If you want to see the edit, delete and permission details that aren’t shown in these screens yet, ask for a walkthrough of those specific flows before rolling Pocket Book out to your team.

    A logbook nobody can search isn’t a record. It’s just paper that happens to be digital, waiting for the one day someone actually needs it and finds nothing there

    See how Pocket Book actually works. Book a quick walkthrough

    CONTACT US

    Website : https://www.avessecurity.com

    Linkedin: https://www.linkedin.com/company/aves-security-management-system/

    Instagram: https://www.instagram.com/avessecurity/

    What is Pocket Book in AVES?

    Pocket Book is a feature under Logs & Reference where guards and managers log short, dated notes. It functions as an electronic guard logbook, not an incident report or occurrence log, for the everyday observations that don’t need formal escalation.

    How do you create a Pocket Book entry?

    From the Home dashboard, go to Logs & Reference, tap Pocket Books, then Create. Fill in a Date, a Time and a Message, then tap Submit.

    What’s the difference between My Books and Staff Books in Pocket Book?

    My Books shows entries the current user logged. Staff Books shows entries logged by staff. They’re separate views, so checking only one can mean missing entries logged under the other.

    Can a Pocket Book entry be edited after it’s submitted?

    That isn’t confirmed in the current screens. Ask for a live demo of that specific flow before assuming how it works.

    Is Pocket Book meant to replace a handwritten security logbook entirely?

    That’s the intent. A digital guard logbook removes the risks paper carries, lost pages, illegible handwriting, no backup, while asking guards to log roughly the same information they already would on paper.

    What happens if you select a date with no entries?

    The screen tells you plainly rather than leaving it blank. Under My Books it shows “No Data Available.” Under Staff Books it shows a slightly longer message, “No Data available for the Selected Date.” Both mean the same thing, no entries exist for that day, but the wording isn’t identical between the two views, so don’t read it as a different kind of result.